TL;DR
AI-enabled attackers started probing WordPress sites within hours of CVE-2026-87902 going public, which is why Miggo treats mitigation, not remediation, as the first move. Here is how Miggo customers on WAF Copilot and AWS WAF closed the exploitability window in under 24 hours, with a rule that held against every exploit variant we threw at it.
Another week, another WordPress core RCE
If it feels like critical vulnerabilities are arriving in clusters lately, that is because they are. After a run of Linux privilege escalations and a string of flaws in AI workflow products like LiteLLM and Langflow, WordPress core has become the next target, starting with wp2shell and now continuing with CVE-2026-87902.
CVE-2026-87902 was published on Tuesday, September 22, and it is a conditional remote code execution vulnerability caused by a local file inclusion flaw in WordPress core. It does not affect every WordPress deployment, but it affects a significant share of them, and because WordPress runs such a large portion of the web, even a conditional flaw in core translates into an enormous number of exposed sites. Attackers understood that immediately and started probing WordPress sites within hours of the patch.
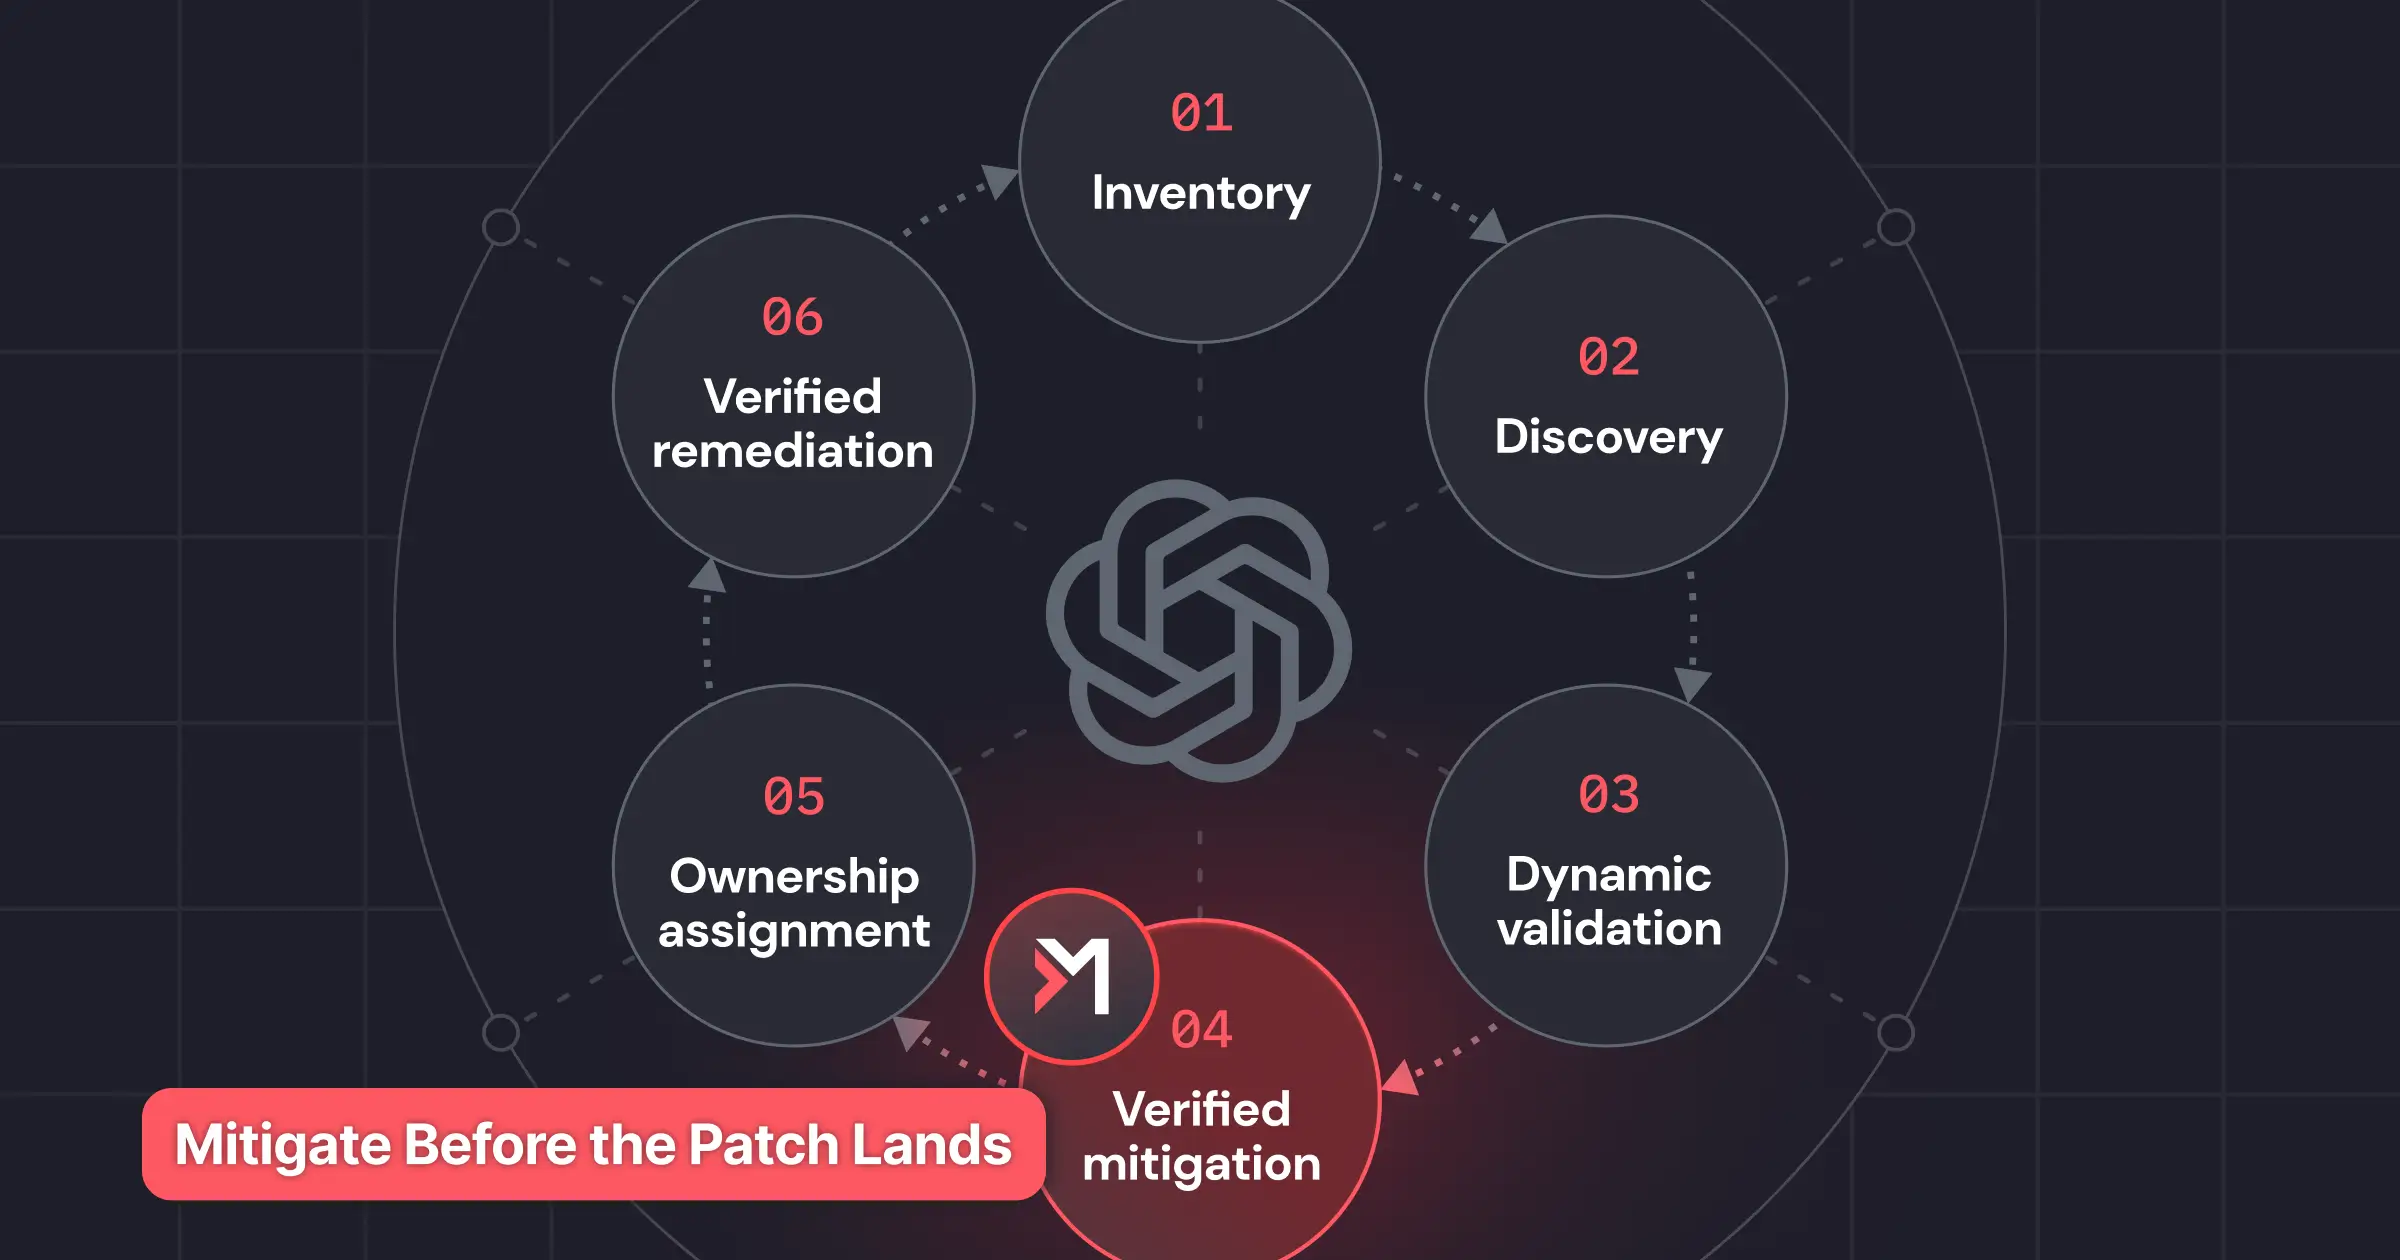
This post is not another technical breakdown (for a great one see Patchstack’s technical breakdown) . It is the story of how in the age of AI enabled exploitation, mitigation must replace remediation as the first course of action to achieve zero exploitability. We’ll cover how Miggo’s customers achieved this through our WAF Copilot and through our partnership with AWS WAF.
The timeline: hours for attackers, days for everyone else
The gap between when a vulnerability becomes usable and when it is actually protected is what we call the exploitability window, and in the case of CVE-2026-87902 you can see exactly how wide it was for teams relying on traditional sources of protection:
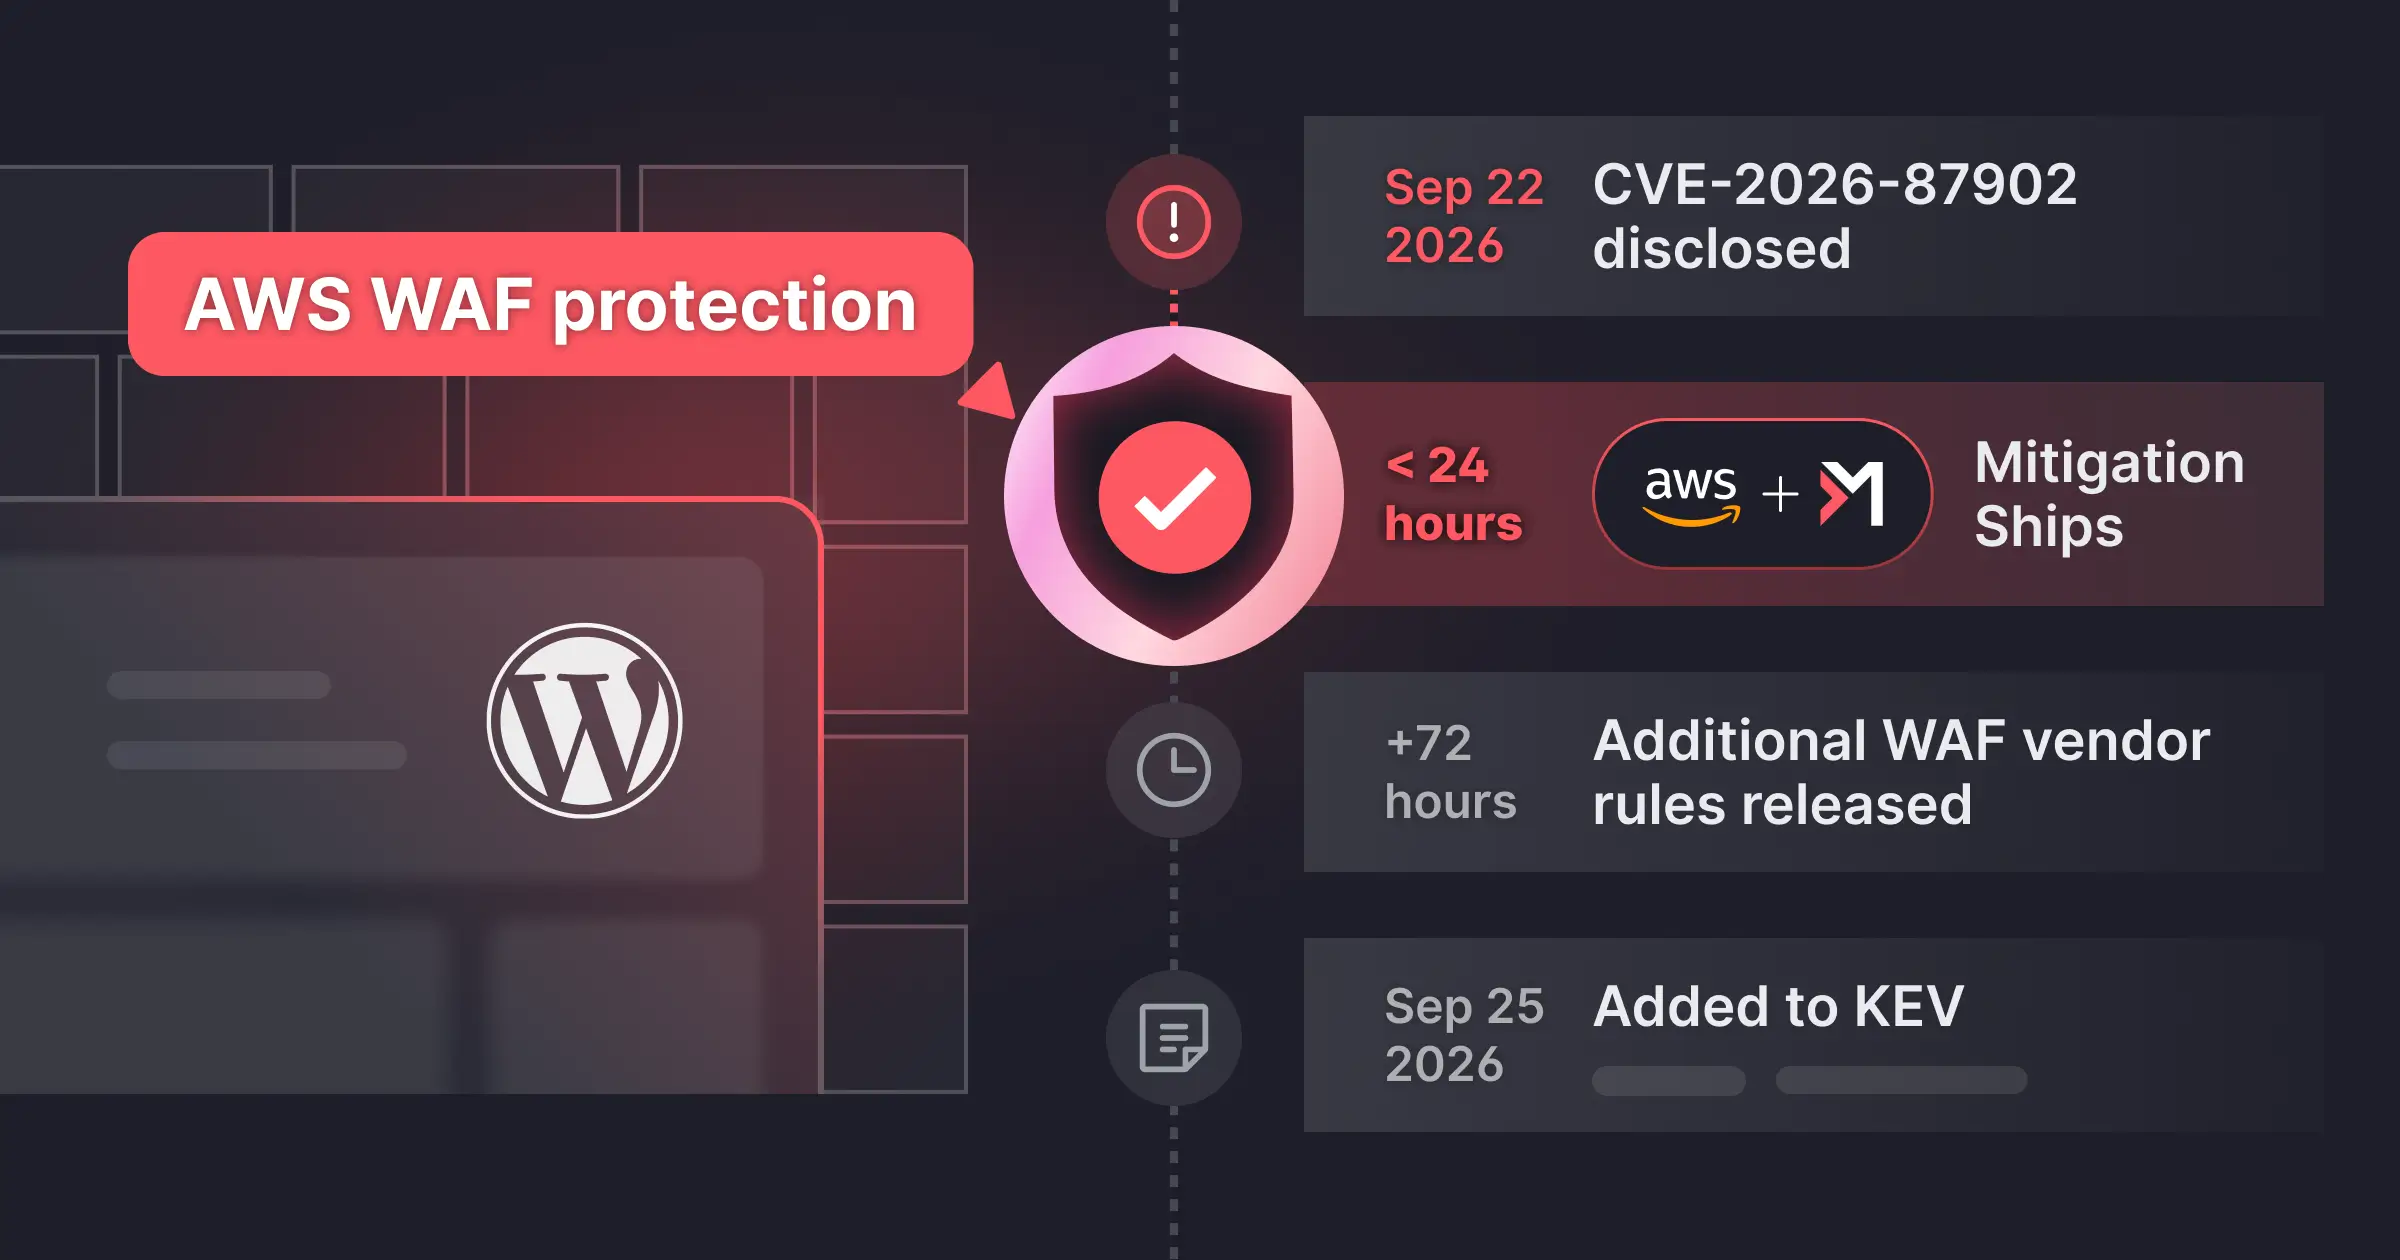
- September 22: CVE-2026-87902 is published, and within a few hours Miggo observes the first exploit for it.
- Within 24 hours of disclosure: Miggo adds a rule covering the CVE to the High Emerging Threats (HET) ruleset for AWS WAF, shipped in version 1.16.
- Roughly 36 hours later: the first emergency rule from a major WAF vendor becomes available to its customers.
- September 25: CISA adds CVE-2026-87902 to the Known Exploited Vulnerabilities (KEV) catalog.
That means teams who waited for their WAF vendor lost a day and a half of protection, and teams who waited for KEV to tell them the threat was real lost roughly three days, all while exploitation was already happening in the wild. This is not unusual anymore, since Mandiant's M-Trends 2026 puts the mean time to exploit at minus seven days, meaning exploitation now routinely begins before a patch even exists.
What the HET ruleset for AWS WAF is
The Miggo Rules for AWS WAF: High Emerging Application Threats ruleset is a partner managed rule group available on AWS Marketplace that delivers exploit-aware protection against the highest-impact and most recent web CVEs, weighted toward KEV additions and actively exploited vulnerabilities. You subscribe once, attach it to your web ACL, and new rules arrive as new threats emerge, so your team does not have to research each vulnerability, write the rule, and test it themselves every time something like CVE-2026-87902 hits the news.
For CVE-2026-87902, that meant AWS WAF customers subscribed to HET received coverage in version 1.16 of the ruleset without writing a single line of rule logic, and well before the rest of the market had anything to deploy. You can read more about the ruleset on the Miggo Rulesets for AWS WAF page.
Fast only matters if the rule holds
Shipping a rule quickly is easy if you are willing to ship a rule that does not work. A rule that can be bypassed is not a mitigation, and neither is a rule so broad that it blocks legitimate traffic and gets switched off by the team that has to live with it. The reason our rule for CVE-2026-87902 was both fast and reliable comes down to how Miggo builds mitigations in the first place.
As soon as a vulnerability is announced, Miggo's agents catalog it, break down its flow to the function level, and run the vulnerable application tied to its real source code in an internal sandbox, so that the analysis rests on runtime truth rather than on a guess about what the exploit might look like. From that model, agents generate rule candidates and iterate on multiple ways of encoding the same logic in each WAF's own syntax and capabilities, which we describe in more detail in our engineering blog.
Because we understand the vulnerability rather than just the first published payload, we can also generate two kinds of traffic to test every rule against: exploit traffic that triggers the vulnerability, and benign traffic made up of normal application flows along with requests that look suspicious but are actually fine. For CVE-2026-87902 we generated more than 200 exploit variants and more than 100 benign traffic patterns, then ran the vulnerable application behind major WAF vendors to see how their protections behaved.
Some of those exploit variants slipped past the rules other vendors shipped, while the Miggo rule blocked every one of them, and a rule that did not pass that bar would never have gone out to customers in the first place. This is the same pattern we documented in our Beat the Bypass report, where the best performing generic managed ruleset blocked 48% of real exploit bypasses and Miggo's environment-specific rules blocked 91%. A generic signature is written against a payload someone has already seen, while a derived mitigation is written against what any exploit must do to reach the vulnerable function, which is why it keeps working when attackers start mutating their payloads.
From one CVE to every exploitable path: Autonomous Mitigation
The HET ruleset is the most visible piece of a much bigger idea, a vulnerability stays usable by an attacker until something actually stops the exploit path from succeeding. Remediation removes the flaw on engineering time, while mitigation closes the exploit path at machine speed, and Miggo exists to own that fast clock through what we call Autonomous Mitigation. For customers on the full Miggo platform, the same engine behind the HET rule proves which vulnerabilities are truly exploitable in their environment, shields them through the controls they already own, and holds that protection, re-tested against new variants and backed by runtime detection and response, until the patch lands.
What to do about CVE-2026-87902 right now
- Mitigate now: If you run WordPress behind AWS WAF, subscribe to the Miggo High Emerging Application Threats ruleset on AWS Marketplace and attach it to your web ACL, and if you already subscribe, confirm you are on version 1.16 or later so the rule for CVE-2026-87902 is active.
- Patch when you’re ready: Update to the latest WordPress release, since mitigation buys you time but remediation is what removes the flaw for good.
- Look back, not just forward. Exploitation started within hours of disclosure, so review your WAF and application logs from September 22 onward for signs of probing or successful exploitation, especially on any site that was not protected in that window.
- Stop waiting on KEV. KEV is a valuable signal that a vulnerability has been exploited, but by the time a CVE lands there, attackers have usually had days to use it, so your response process needs to start at disclosure rather than at confirmation.
- Don't rely on a single layer. Even the best WAF rule is one control, so pair it with detection inside the application, which catches exploitation based on how attacks behave rather than on which CVE they target to achieve defense in depth.
Just another Tuesday
It would be comforting to believe that the recent wave of critical vulnerabilities is an anomaly that will pass if we can just hold on, but everything we are seeing points the other way, with more catastrophic flaws arriving faster and the time to exploit dropping below zero. For attackers, CVE-2026-87902 was just another Tuesday, and the only sustainable answer is for it to be just another Tuesday for defenders too, which means protection that arrives in hours, holds up against every variant, and stays in place until the patch is ready.
That is what Miggo delivered for AWS WAF customers on CVE-2026-87902, and it is what Autonomous Mitigation delivers across your entire environment. Vulnerabilities are inevitable, but standing exploitability is not. Book a demo to see how Miggo can close your exploitability window.