Blog

Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
0 results matching
tag
NGINX HTTP/2 RCE (CVE-2026-123633, CVE-2026-123007): What We Know and How to Get Protected Before You Patch

Security
Research
Two critical NGINX HTTP/2 flaws, CVE-2026-123633 and CVE-2026-123007, allow unauthenticated remote code execution. What is public so far, who is exposed, and how to get protected before you patch.
Read More
Java4Shell (CVE-2026-114938) blog header

Java4Shell (CVE-2026-114938): What We Know and How to Get Protected Before the Patch

Blog
Java4Shell (CVE-2026-114938) is a critical OpenJDK runtime flaw. What is public so far, who is exposed, and how to get protected before the patch.
Read More

ARTEX Attacks on South Korean Banks: What You Need to Know and How to Stay Protected

Security
Research
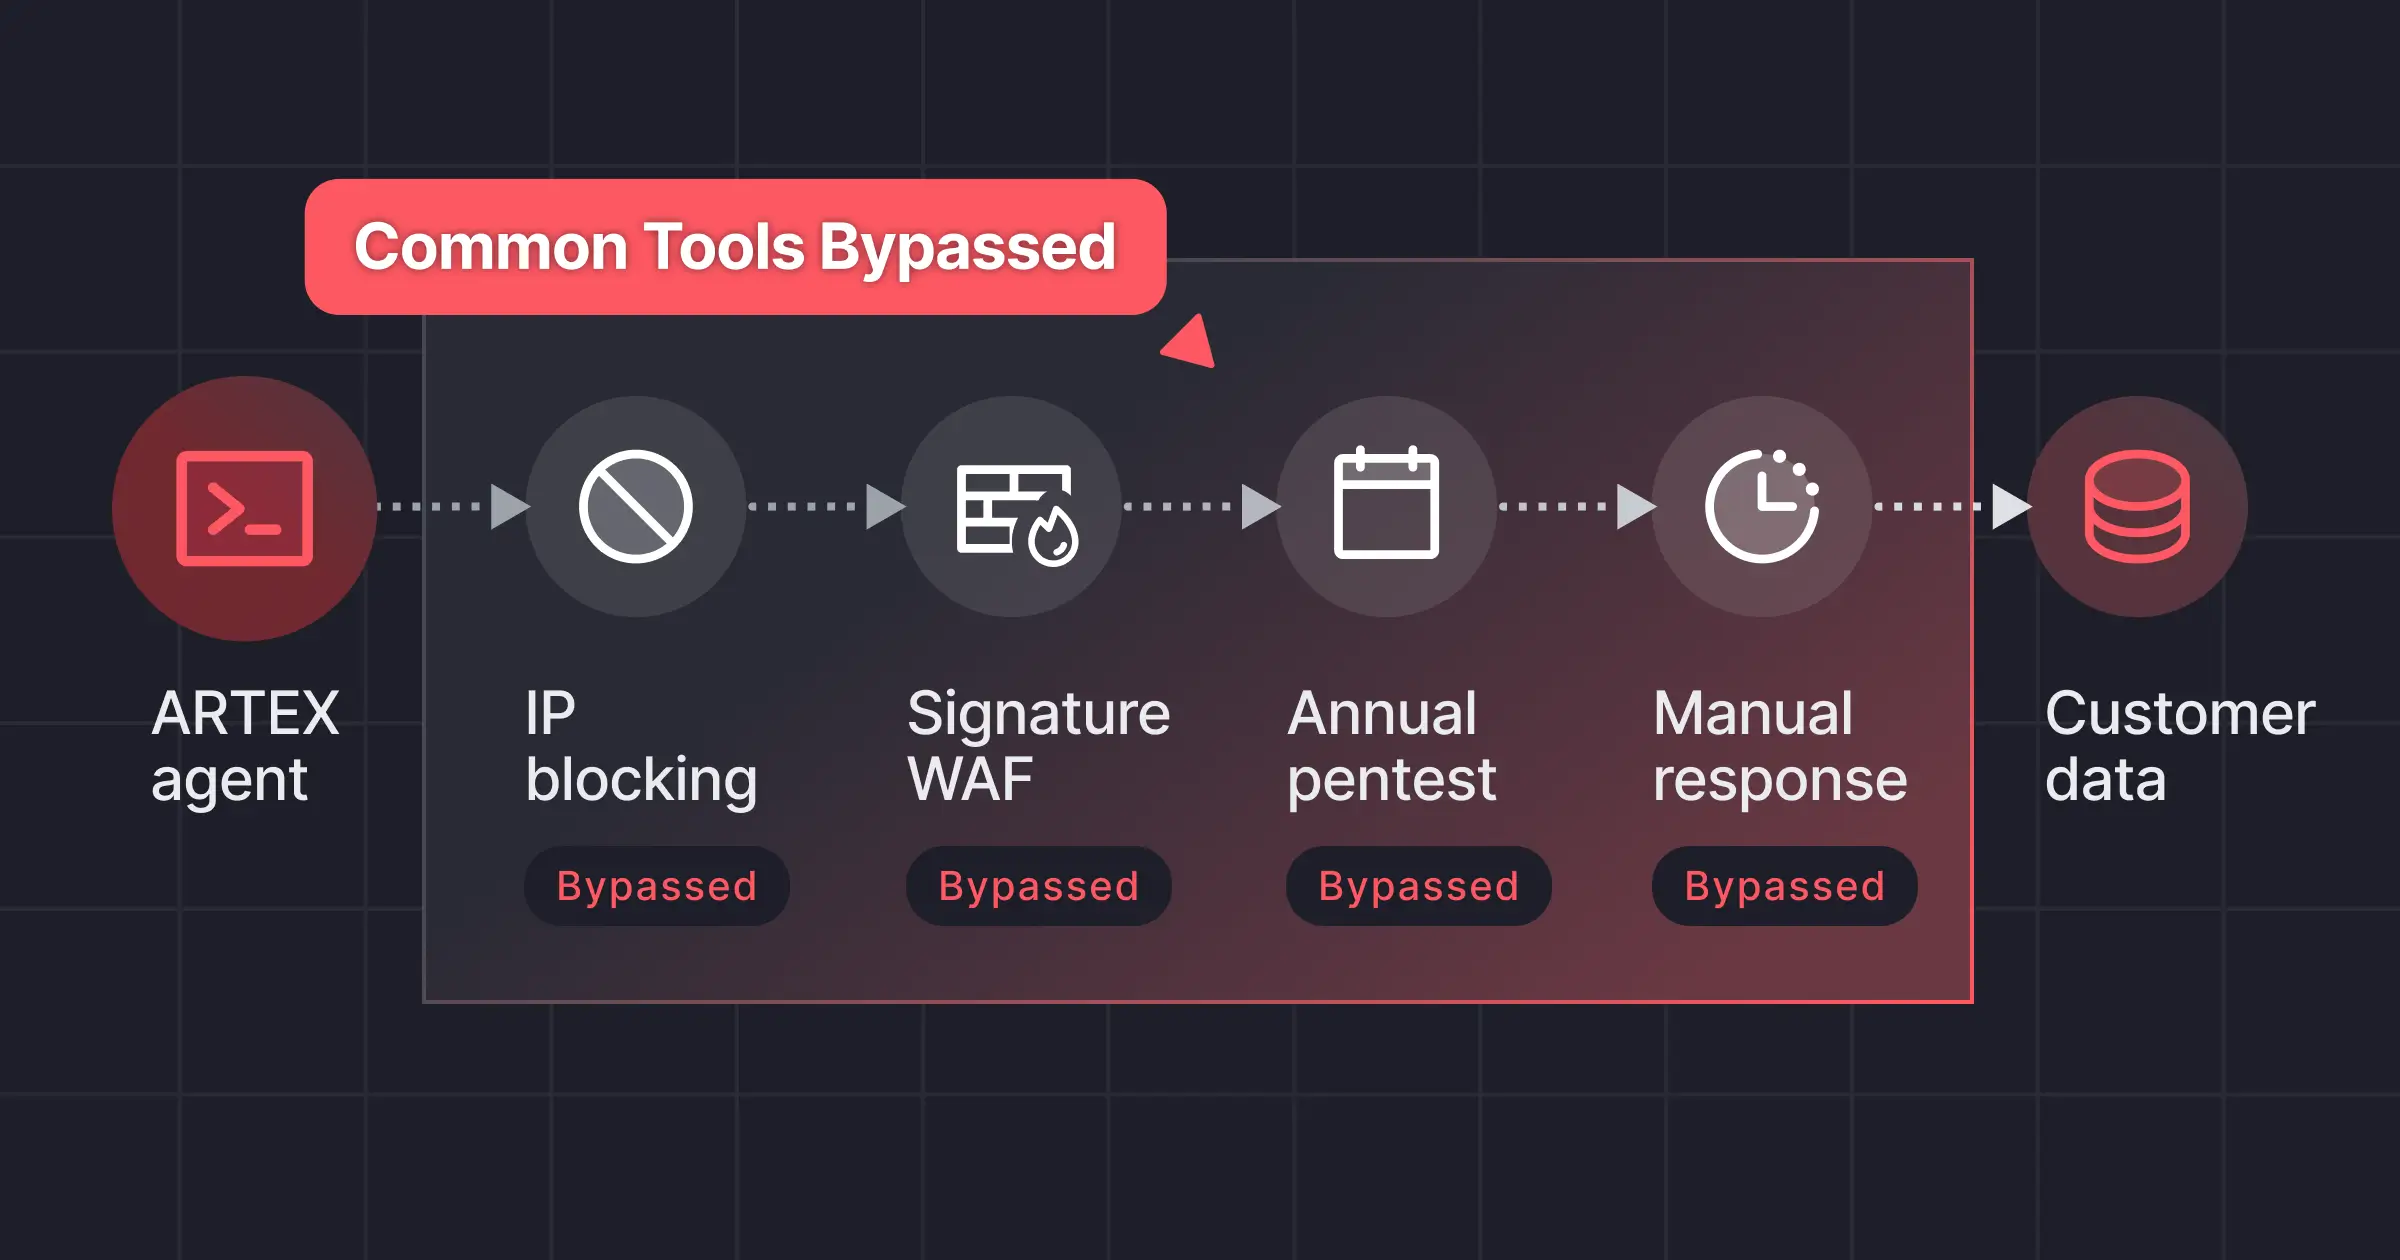
An AI agent called ARTEX was tied to breaches at Korean financial firms through broker and staff apps. How it worked and what banks should check now.
Read More

Miggo Security Joins the Wiz Integration Network

Product
Miggo Joins Wiz Integration Network to help customers reduce cloud risk and mitigate exploitable vulnerabilities before the patch lands.
Read More

Gartner’s Top Strategic Technology Trends for 2027: Autonomous Exposure Remediation | The Road Starts with Mitigation

Security
Research
Gartner® has named Autonomous Exposure Remediation (AER) one of its Top Strategic Technology Trends for 2027. This post walks through our understanding of the report and shows where we feel Autonomous
Read More

PHP2Shell from the Inside: Watch Miggo Detect & Block the Exploit

Security
Research
See how Miggo detects and blocks PHP2Shell exploits at runtime, providing Defense in Depth without changing application code.
Read More

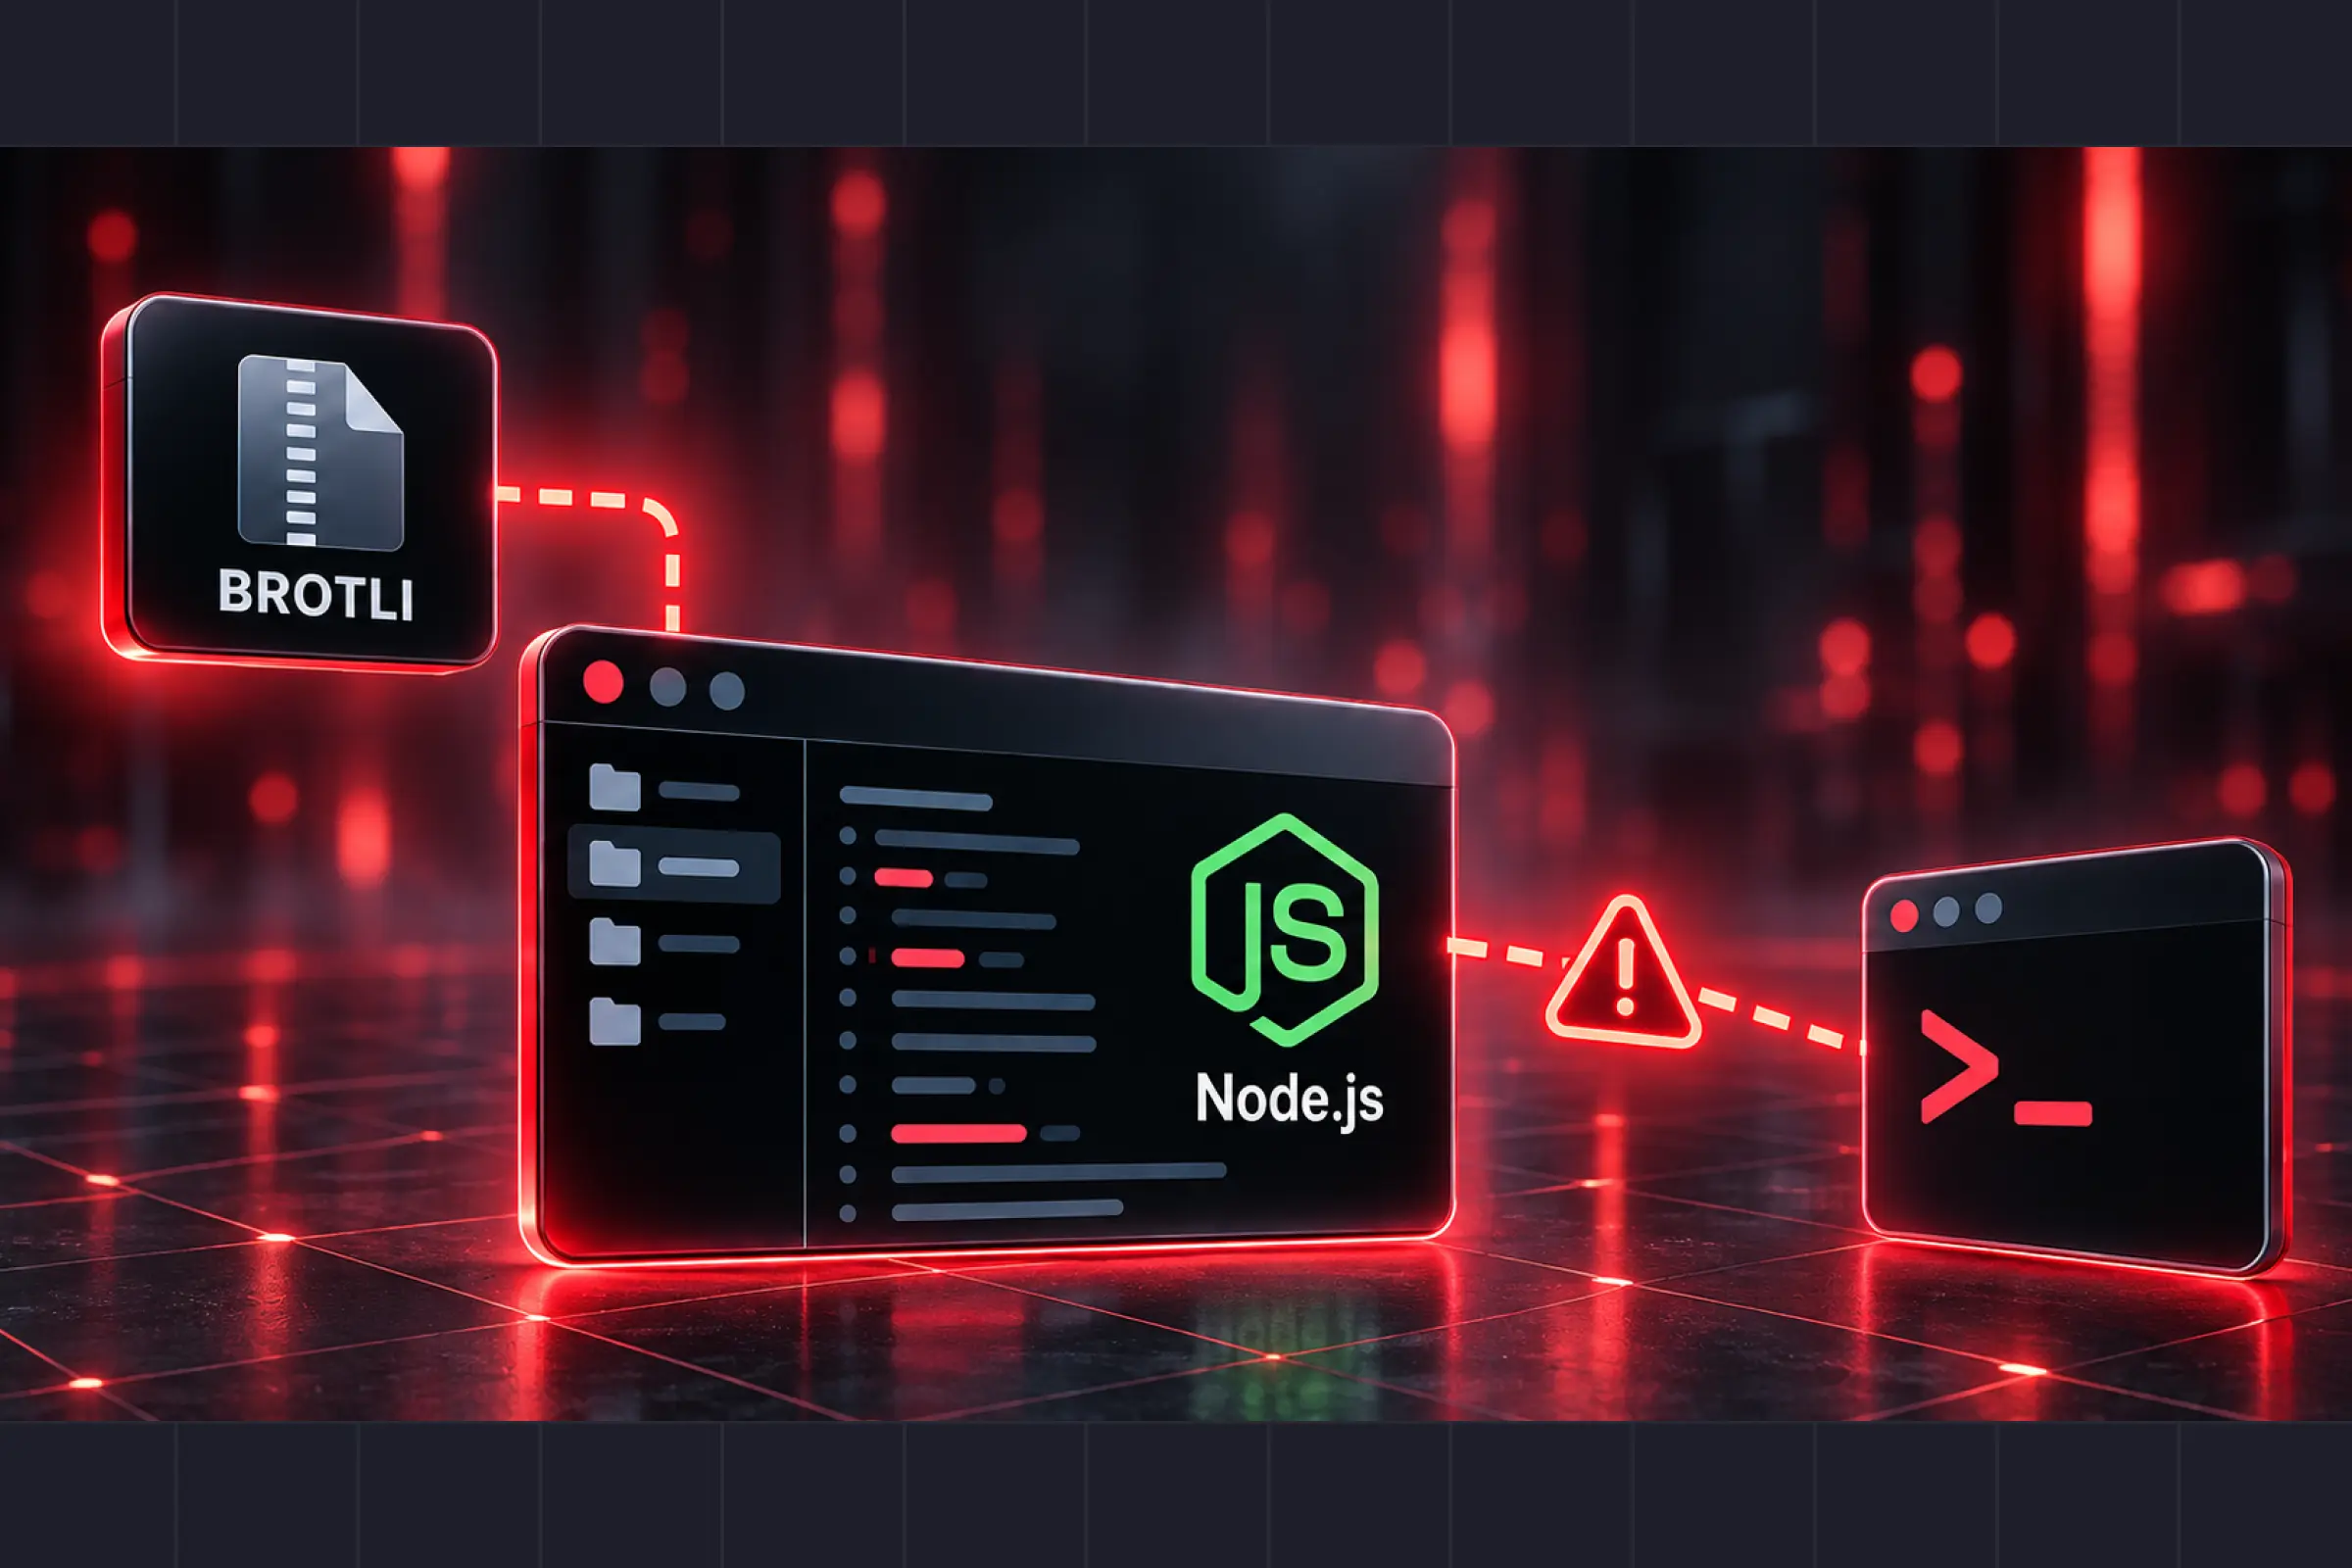
One Compressed Request, No Login: Inside Node2Shell, the Eight-Year-Old Bug in Node.js’s Brotli Decoder

Blog
A Brotli bug hidden in Node.js since 2018 lets one compressed request or fetched response crash a server. See who is exposed and how to fix it.
Read More

PHP2Shell FAQ (CVE-2026-109618, CVE-2026-109619)

Blog
PHP2Shell FAQ: who is vulnerable, what CVE-2026-109618 and CVE-2026-109619 mean, what to do now, and whether WAF rules are enough while you patch.
Read More

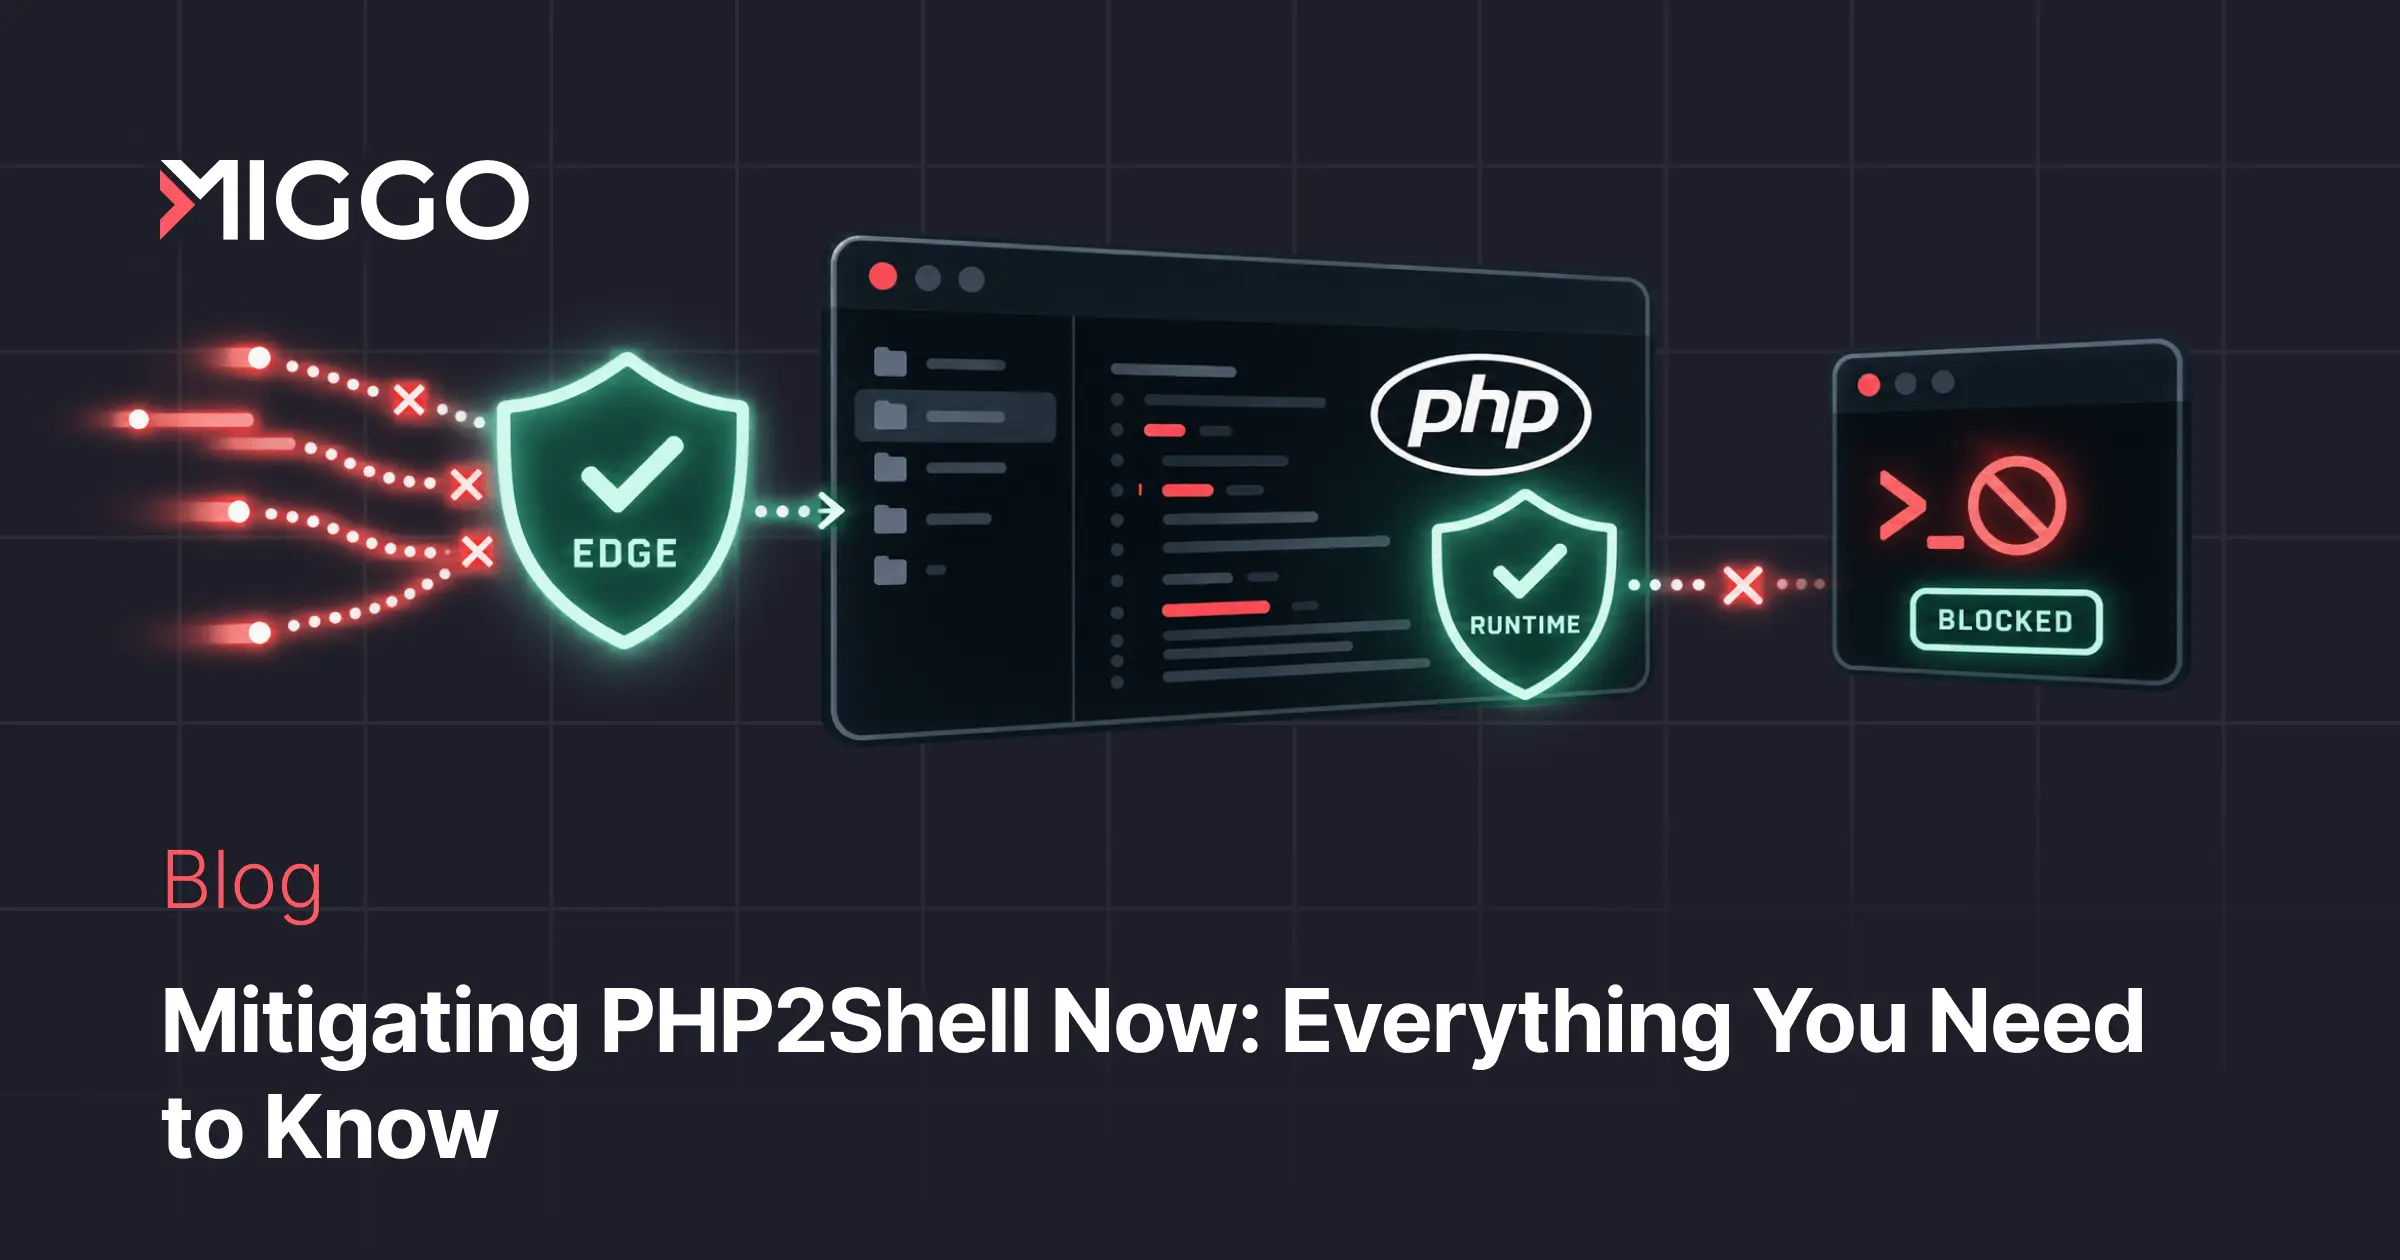
Mitigating PHP2Shell Now: Everything You Need to Know

Blog
PHP has shipped some fixes for PHP2Shell. This post explains what the patch covers, why patching alone is not enough, and how to keep your applications protected.
Read More

PHP2Shell: What We Know and What to Do Before the Patch

Blog
Details of two critical remote code execution flaws in PHP leaked online on October 20, ahead of coordinated disclosure.
Read More

Autonomous Mitigation, Defined: Whitepaper on Closing the Exploitability Window

Security
Research
The paper sets out what Autonomous Mitigation is, the standard for doing it safely, and the metric that shows whether your exposure window is actually closed.
Read More

The Moat Was Scarcity: Part 2

Security
AI erases the time between vulnerability discovery and exploitation. Defenders still have an advantage: Here’s how to turn that knowledge into protection before a patch lands.
Read More