Blog

Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
0 results matching
tag

Miggo Security Recognized as a SINET16 Honoree for Advancing Mitigation-First Runtime Defense

Company
Miggo Security named a 2026 SINET16 Honoree for autonomous mitigation that protects applications from AI-enabled attacks before patches are ready.
Read More

Miggo Security Welcomes Cathy Grim as VP of Customer Success

Company
Miggo builds its customer success function around measurable outcomes, not headcount.
Read More

Mitigation vs. Remediation: What's the Difference and Why You Need Both

Security
Mitigation stops attackers now while remediation takes time. Learn how a mitigation-first approach helps security teams reduce exposure and risk.
Read More

The Moat Was Scarcity: Part 1

Security
AI is making vulnerability discovery and exploitation cheap and fast, shrinking the patch window beyond what patch-speed defense can survive.
Read More
Ask the Attacker: How an authorization check in Veeam Backup & Replication became the exploit. CVE-2026-44963, and one domain password.

The Backup that Backfired: How One Whitelisted ObjRef Hands Any Veeam Domain User SYSTEM (CVE-2026-44963)

Research
CVE-2026-44963 in Veeam Backup & Replication enables SYSTEM-level code execution through a vulnerable .NET Remoting service.
Read More

Defense-in-Depth in Action: How to Stop the LiteLLM Chain (CVE-2026-47101, CVE-2026-47102, CVE-2026-40217) with Panache

Security
See Defense-in-Depth in action as Miggo stops a chained LiteLLM attack spanning authorization bypass, privilege escalation, and RCE.
Read More

An Autonomous Agent Ran 17,600 Actions Against Hugging Face. How to Block Attacks Like It.

Security
AI agents now execute thousands of attack attempts. Miggo identifies the critical application code path and blocks exploitation at runtime.
Read More

Miggo’s Emerging Threat and AI/ML Partner Rulesets Now Available Directly Within AWS WAF

Product
Miggo's partner-managed rule sets bring exploit-aware, continuously updated coverage for CVEs and AI attacks to AWS WAF customers natively
Read More

Miggo Security Defense-in-Depth Mitigation Solution Closes the Patch Gap in Minutes

Product
New approach applies coordinated edge and in-application mitigation, swiftly stopping active exploits while patching moves forward.
Read More
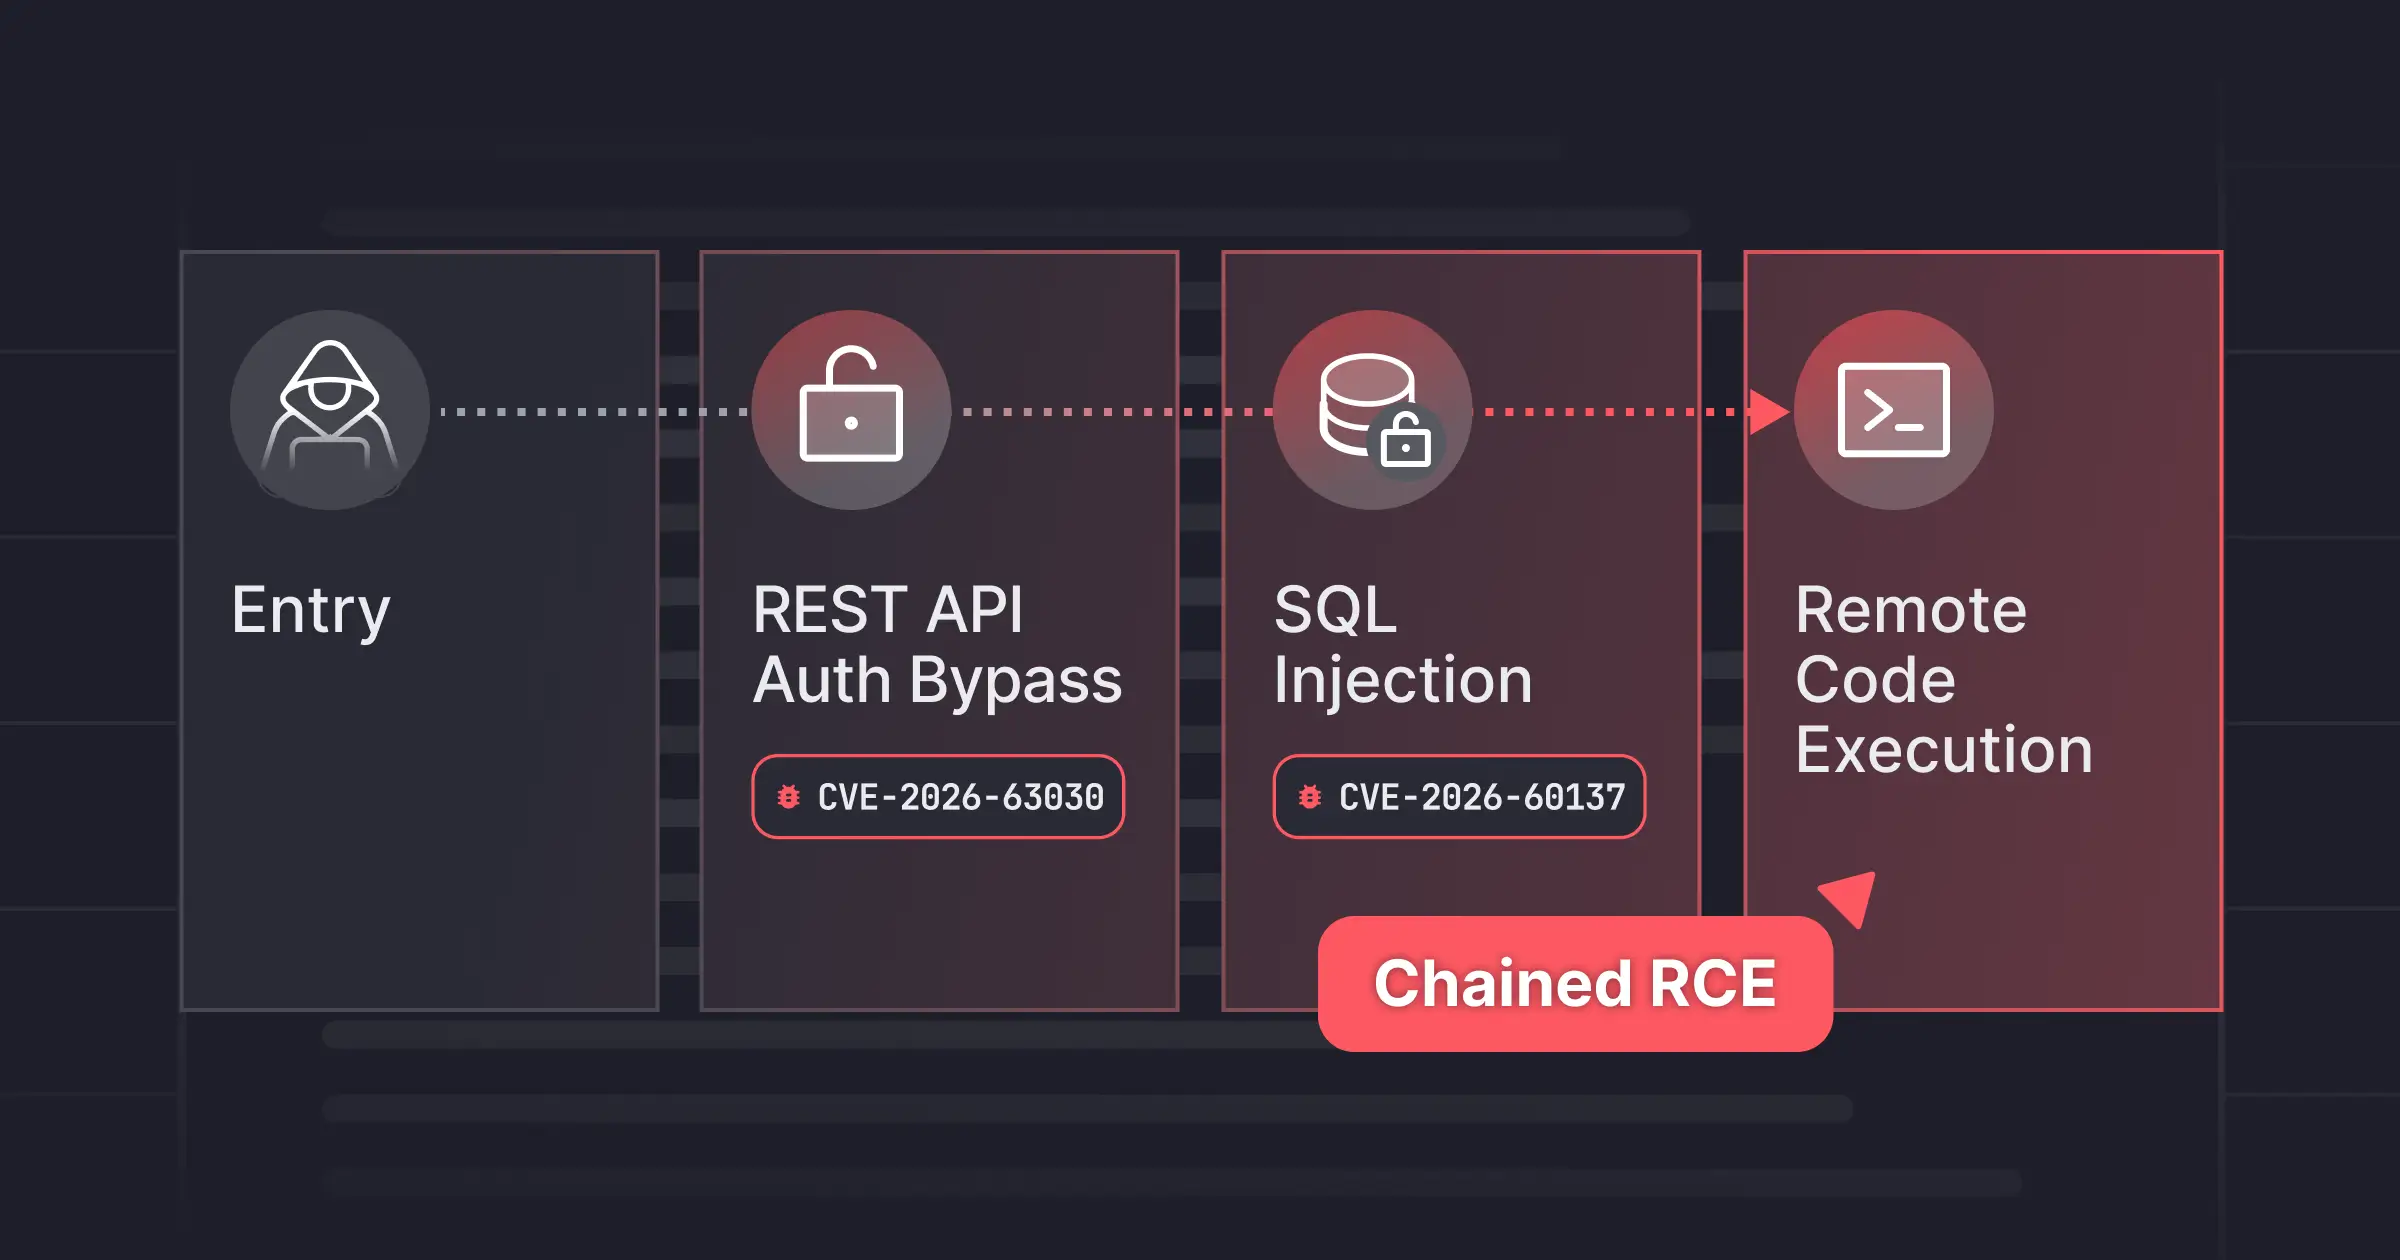
WordPress, No Login Required: Inside wp2shell (CVE-2026-60137 & CVE-2026-63030)

Every WordPress Site's Nightmare: Pre-Auth RCE via wp2shell

Security
Research
A stock WordPress install can be taken over by one anonymous request. Inside wp2shell: CVE-2026-60137 + CVE-2026-63030.
Read More

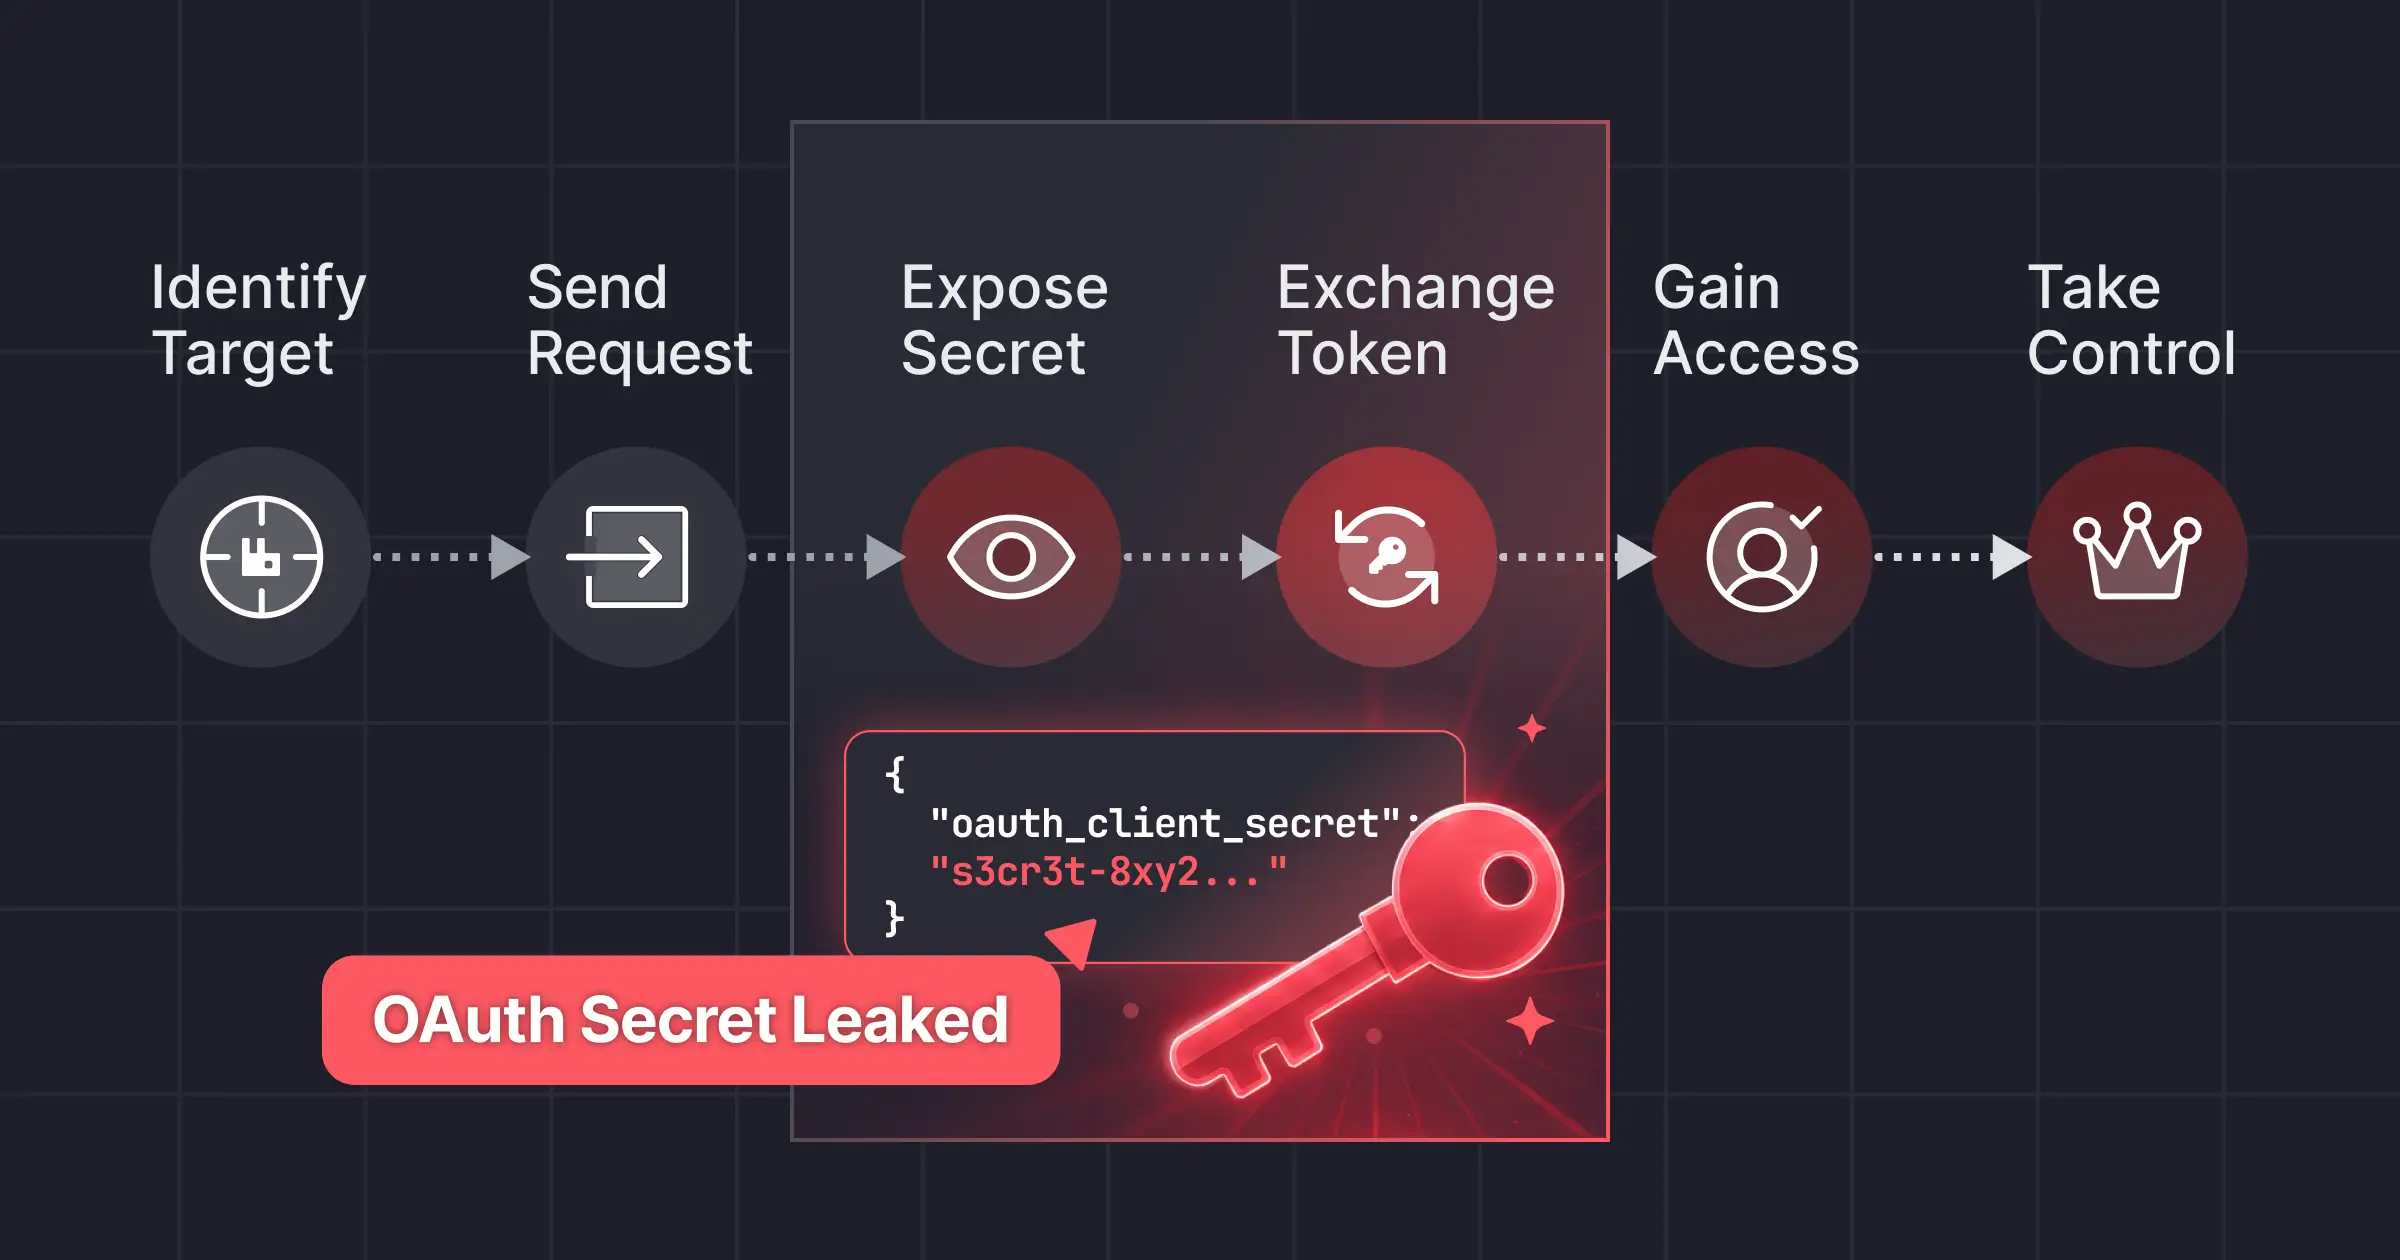
Full Broker Takeover, No Login Required: Miggo Discovers Critical RabbitMQ Vulnerabilities Putting Application Data at Risk

Security
Research
Miggo uncovered two critical RabbitMQ flaws enabling unauthenticated broker takeover and tenant data exposure. Learn who is affected.
Read More

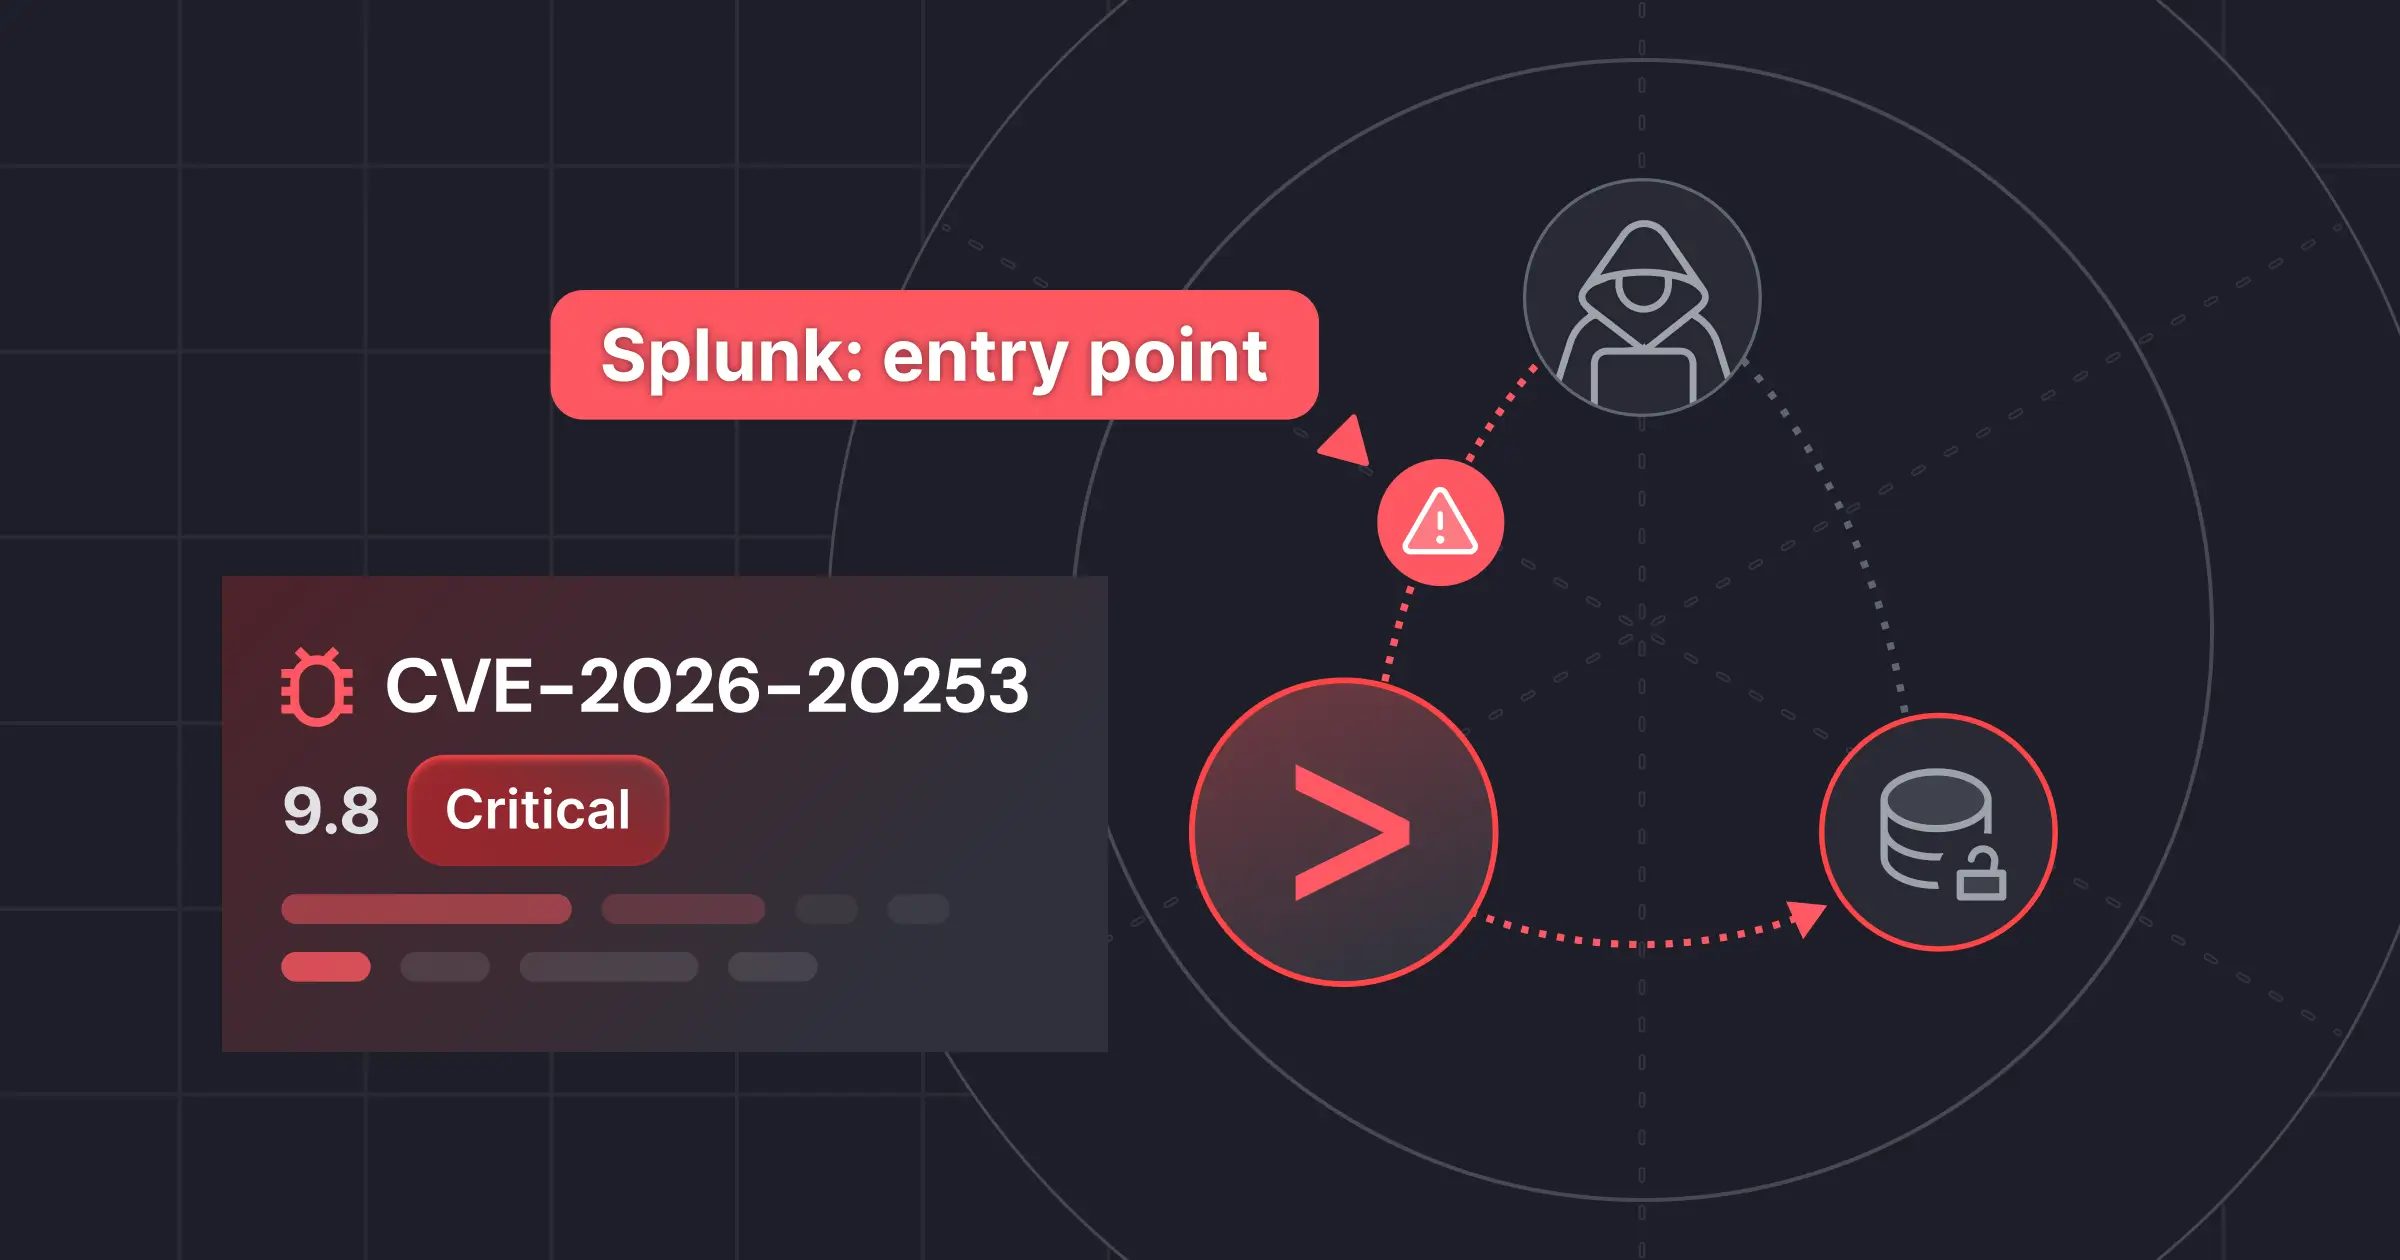
Blind the Watcher: Stopping the Unauthenticated Splunk RCE (CVE-2026-20253) Before the Patch Lands

Security
Research
CVE-2026-20253 turns Splunk Enterprise into an unauthenticated way in. Learn how the exploit works and how Miggo blocks it.
Read More