Oops! Something went wrong while submitting the form.
The Moat Was Scarcity: Part 2
AI erases the time between vulnerability discovery and exploitation. Defenders still have an advantage: Here’s how to turn that knowledge into protection before a patch lands.
Read More
Security
Latest Posts
0 results matching
tag
Miggo Security Welcomes Jamie Taylor as VP of Sales
Company
Miggo Security welcomes Jamie Taylor as VP of Sales to accelerate go-to-market and growth in AI-driven runtime defense and ADR.
Read More
CVE-2026-40175: How Miggo Sees Beyond the CVSS 10.0 Base Score
Security
CVE-2026-40175 scores a 10.0, but real-world risk is far lower. Here’s why context matters more than severity.
Read More
Anthropic Released Its Security Guide Amid the Mythos Madness — and Its Recommendations Sound Familiar
Security
Anthropic’s guide on AI-driven threats closely mirrors modern AppSec realities — and aligns with Miggo’s approach.
Read More
Bridge the DevSec Divide: Using Grafana Cloud and Miggo for Runtime Protection
Product
Grafana Labs and Miggo Security partner on a joint solution built on production telemetry in Grafana Cloud to deliver evidence-based runtime security.
Read More
Miggo Security Extends Runtime Defense for AI and Agentic Observability, Detection and Response
Product
AI apps are non-deterministic; traditional security is blind to them. Miggo's new Agentic DR secures the execution layer of your AI and MCP agents.
Read More
Miggo Security and Grafana Labs Partner to Deliver Frictionless Runtime Intelligence and Slash Vulnerability Noise by 90%
Product
New co-engineered offering enables Grafana Cloud customers to turn already-in-place observability telemetry into AI runtime security
Read More
Hack the AI Brain: Uncovering an Account Takeover Vulnerability in LangSmith
Security
Research
Miggo Security discovered a critical account takeover vulnerability (CVE-2026-25750) in LangSmith. Learn how this flaw exposed proprietary AI data.
Read More
Introducing AI Runtime Observability: Gaining Visibility into AI Sprawl in Production
Company
AI agents change at runtime, creating unseen risk. AI Runtime Observability helps teams detect drift, enforce safety, and govern AI in production.
Read More
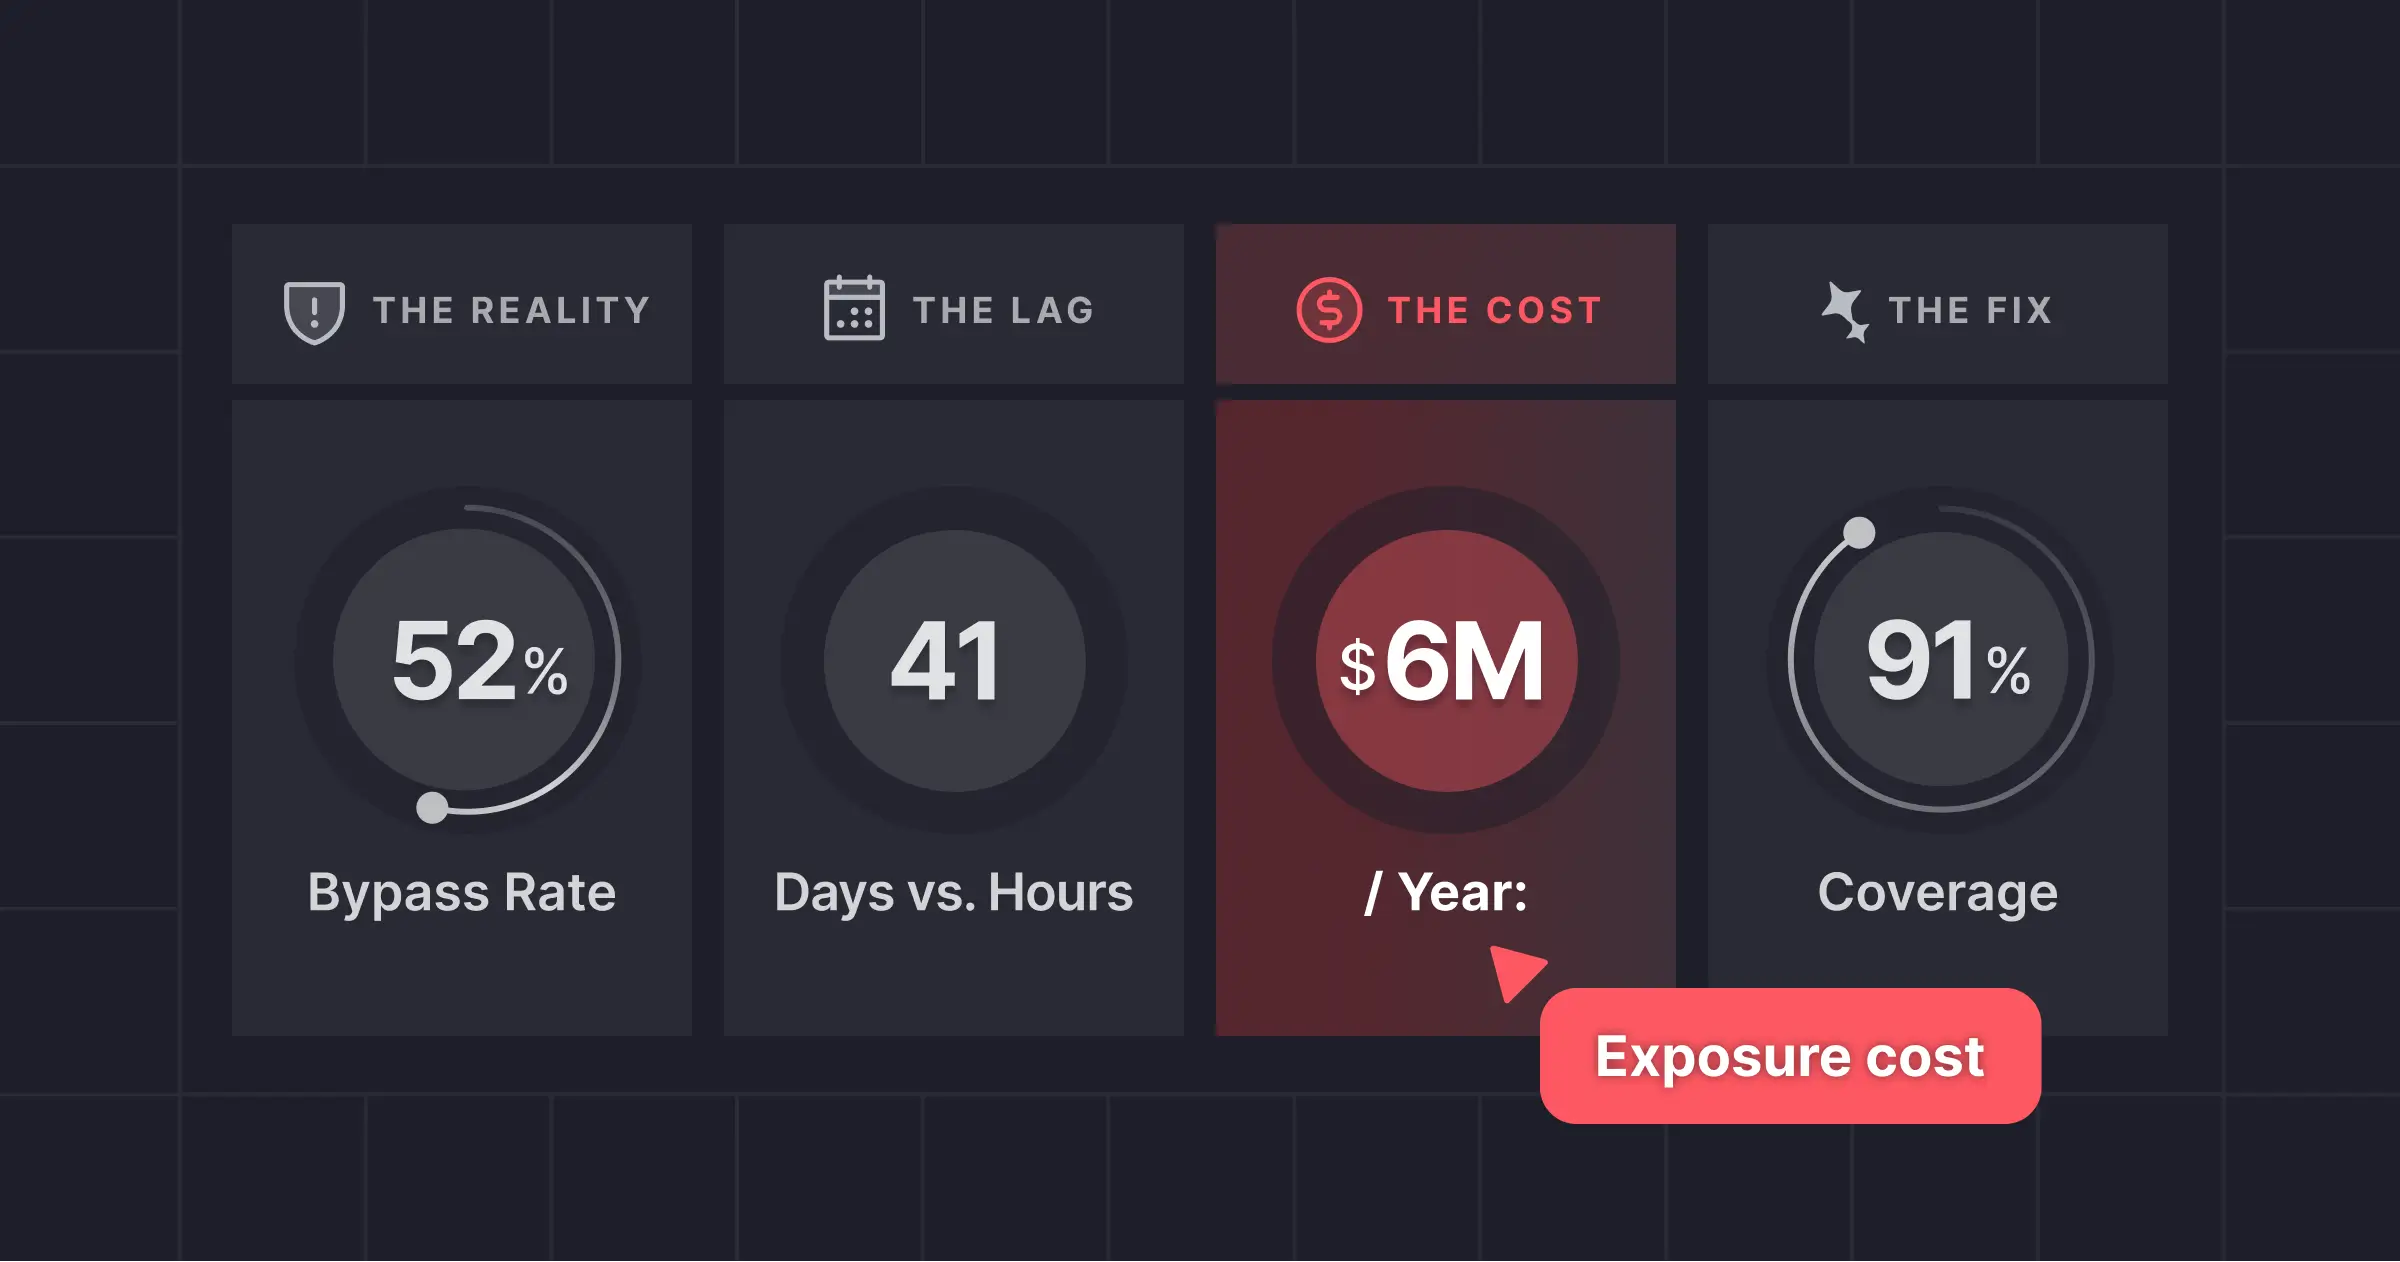
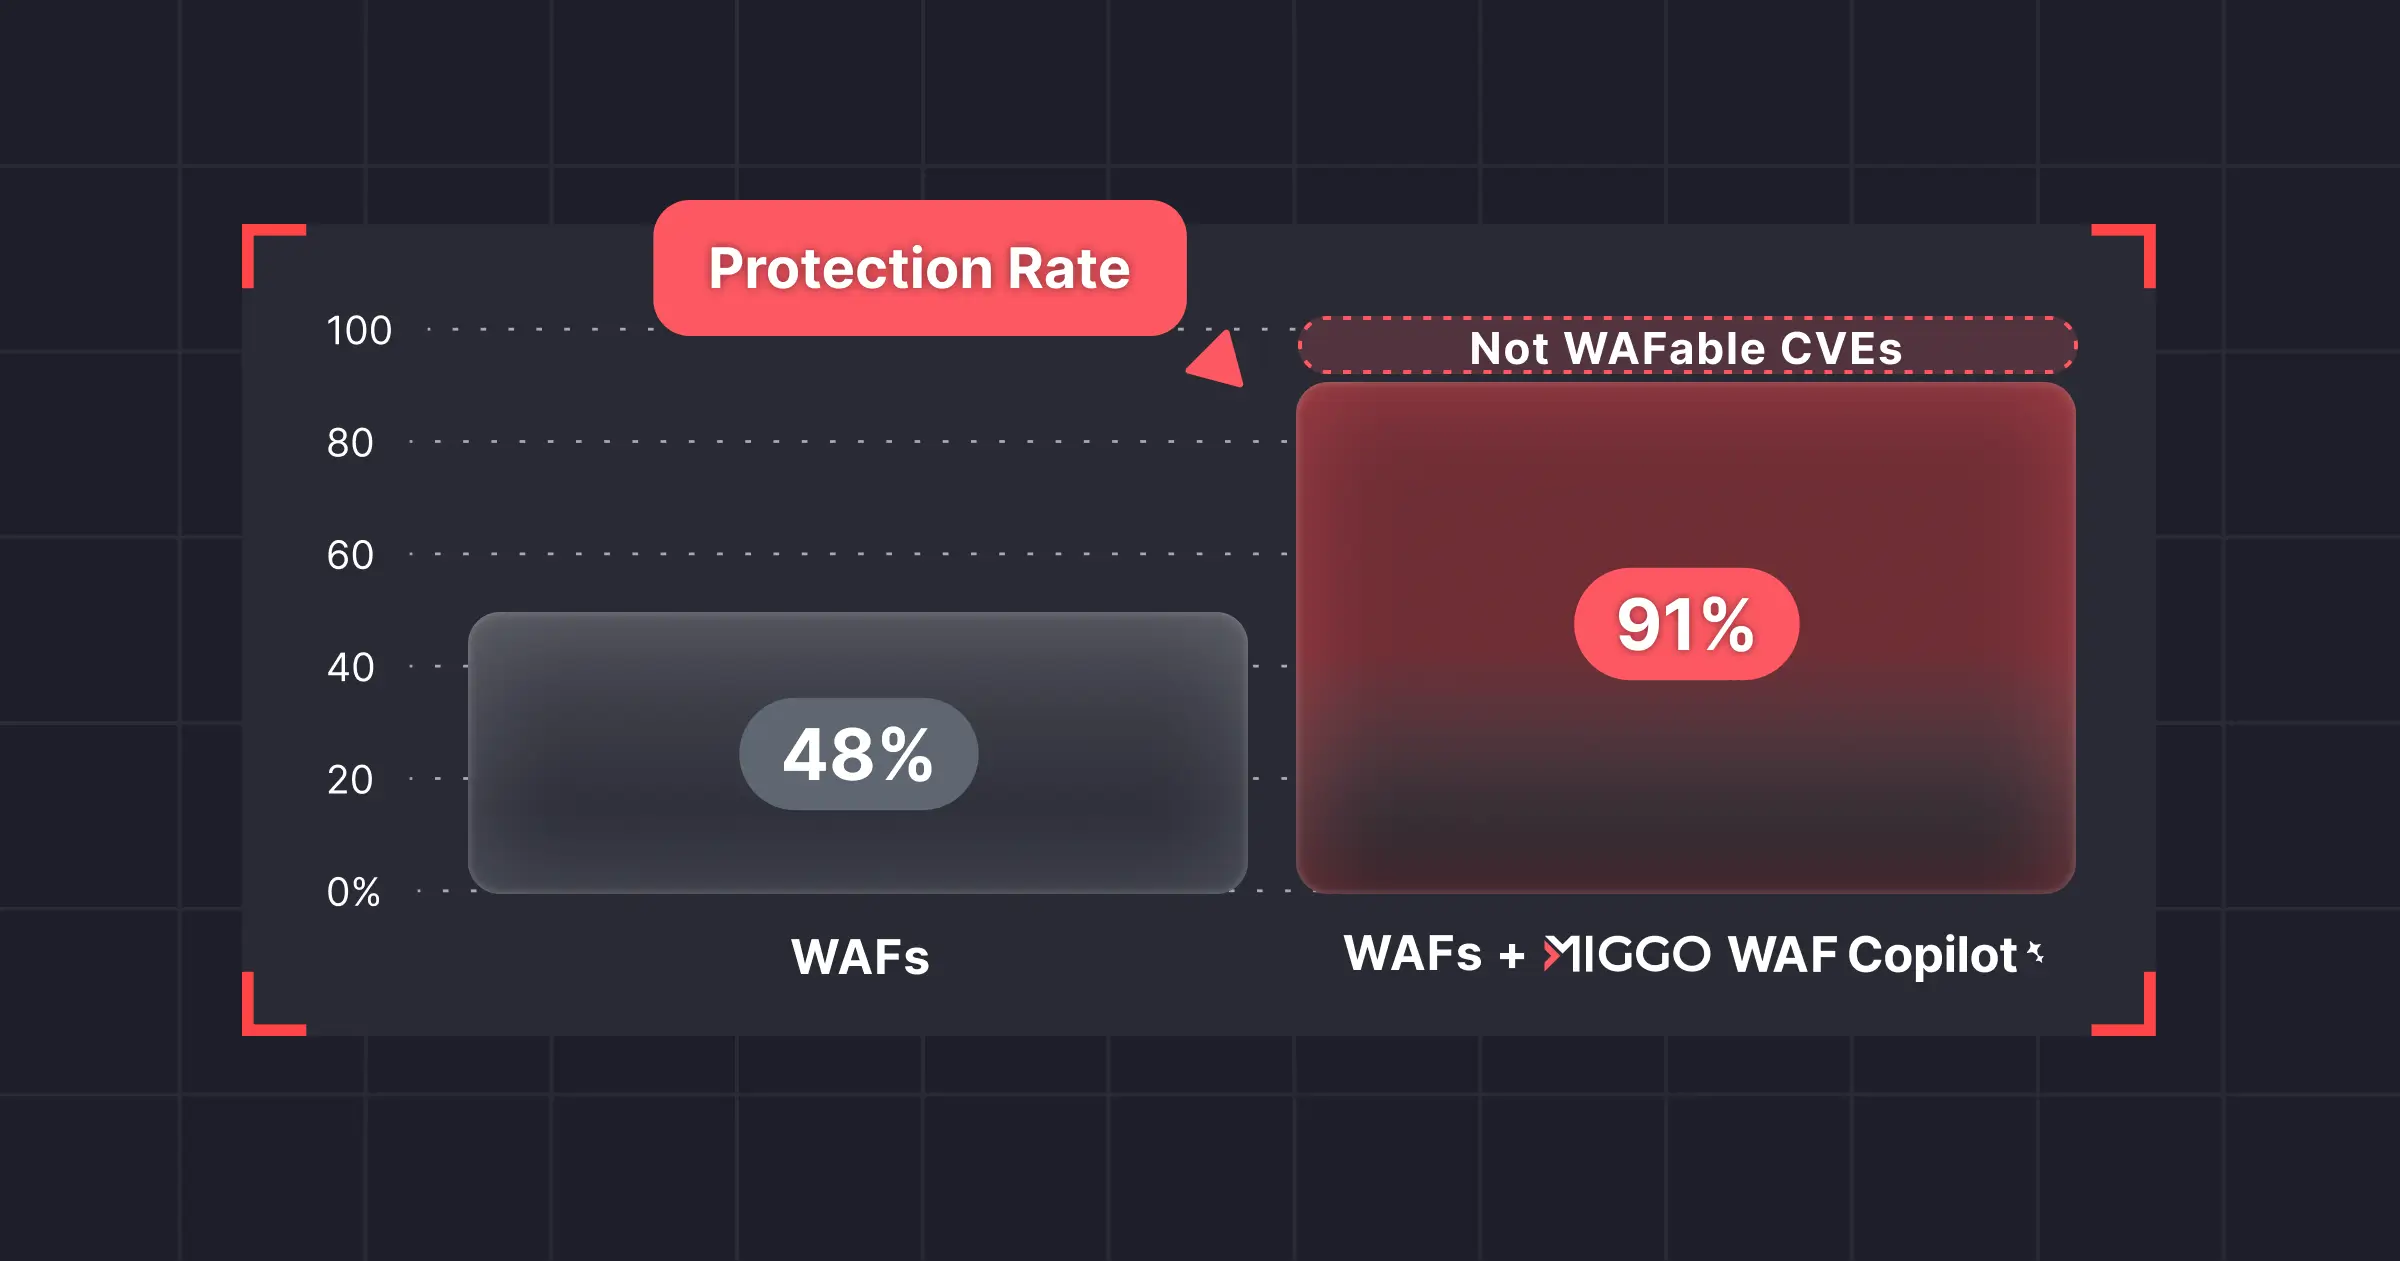
The $6M Exposure Gap: How Your WAF Can Mitigate Vulnerability Attacks in Your Environment
Research
Security
The React2Shell crisis proved it: traditional WAFs miss 52% of exploits. Discover how to close the $6M exposure gap with AI-native run
Read More
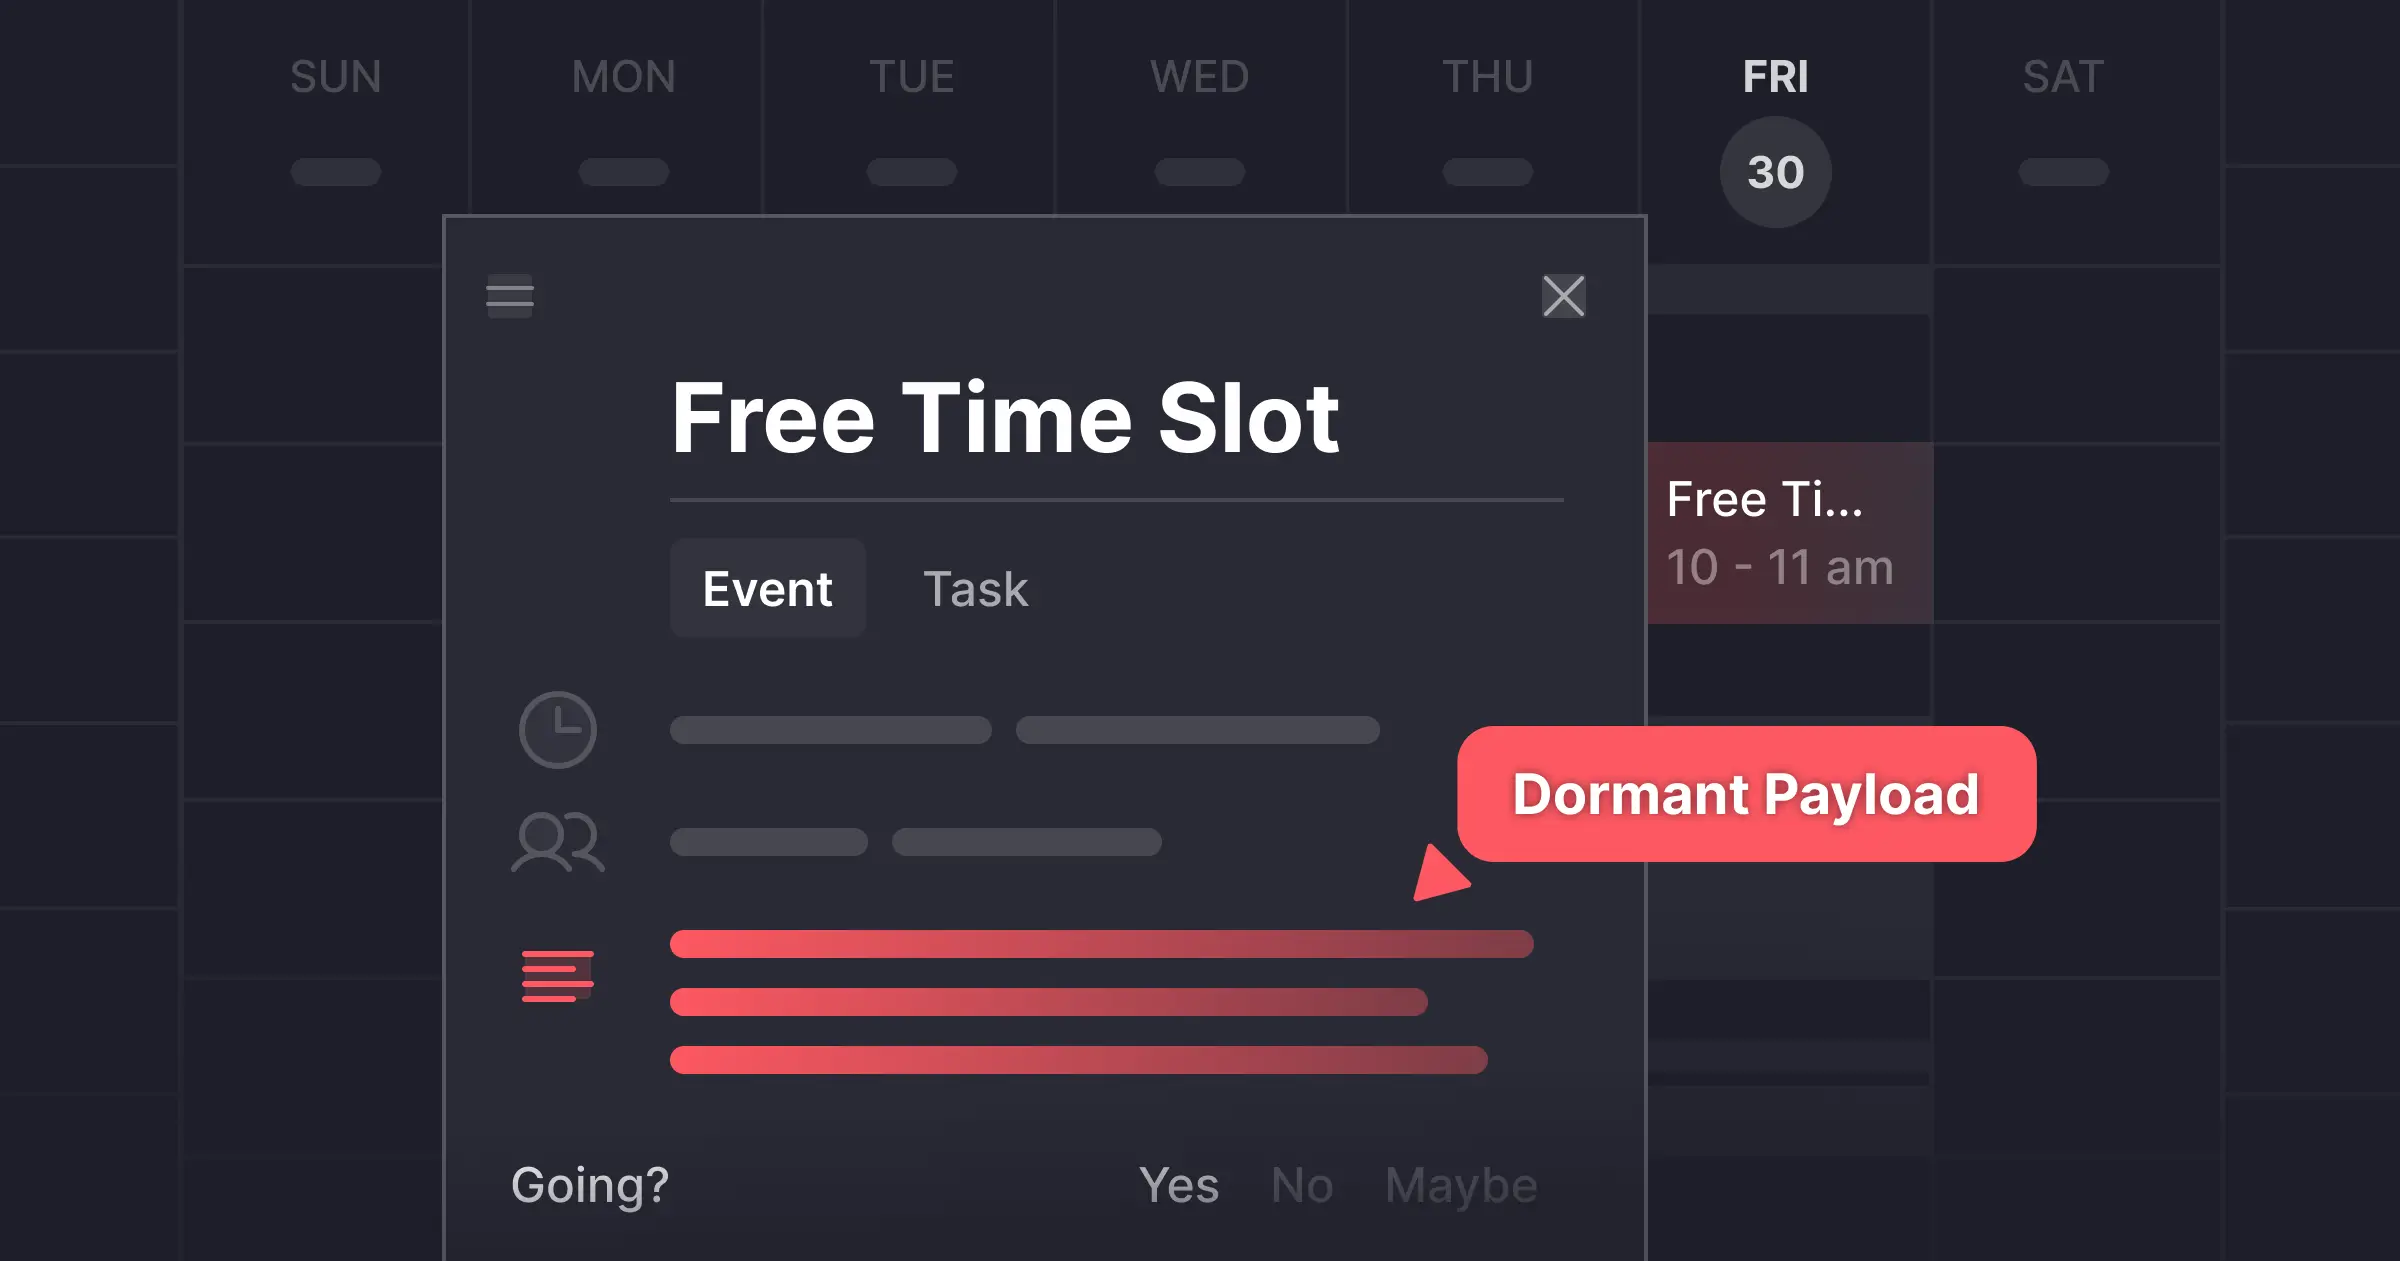
Weaponizing Calendar Invites: A Semantic Attack on Google Gemini
Security
Research
A standard calendar invite became an attack vector, exposing how prompt injection in Google Gemini bypassed privacy controls through language alone.
Read More
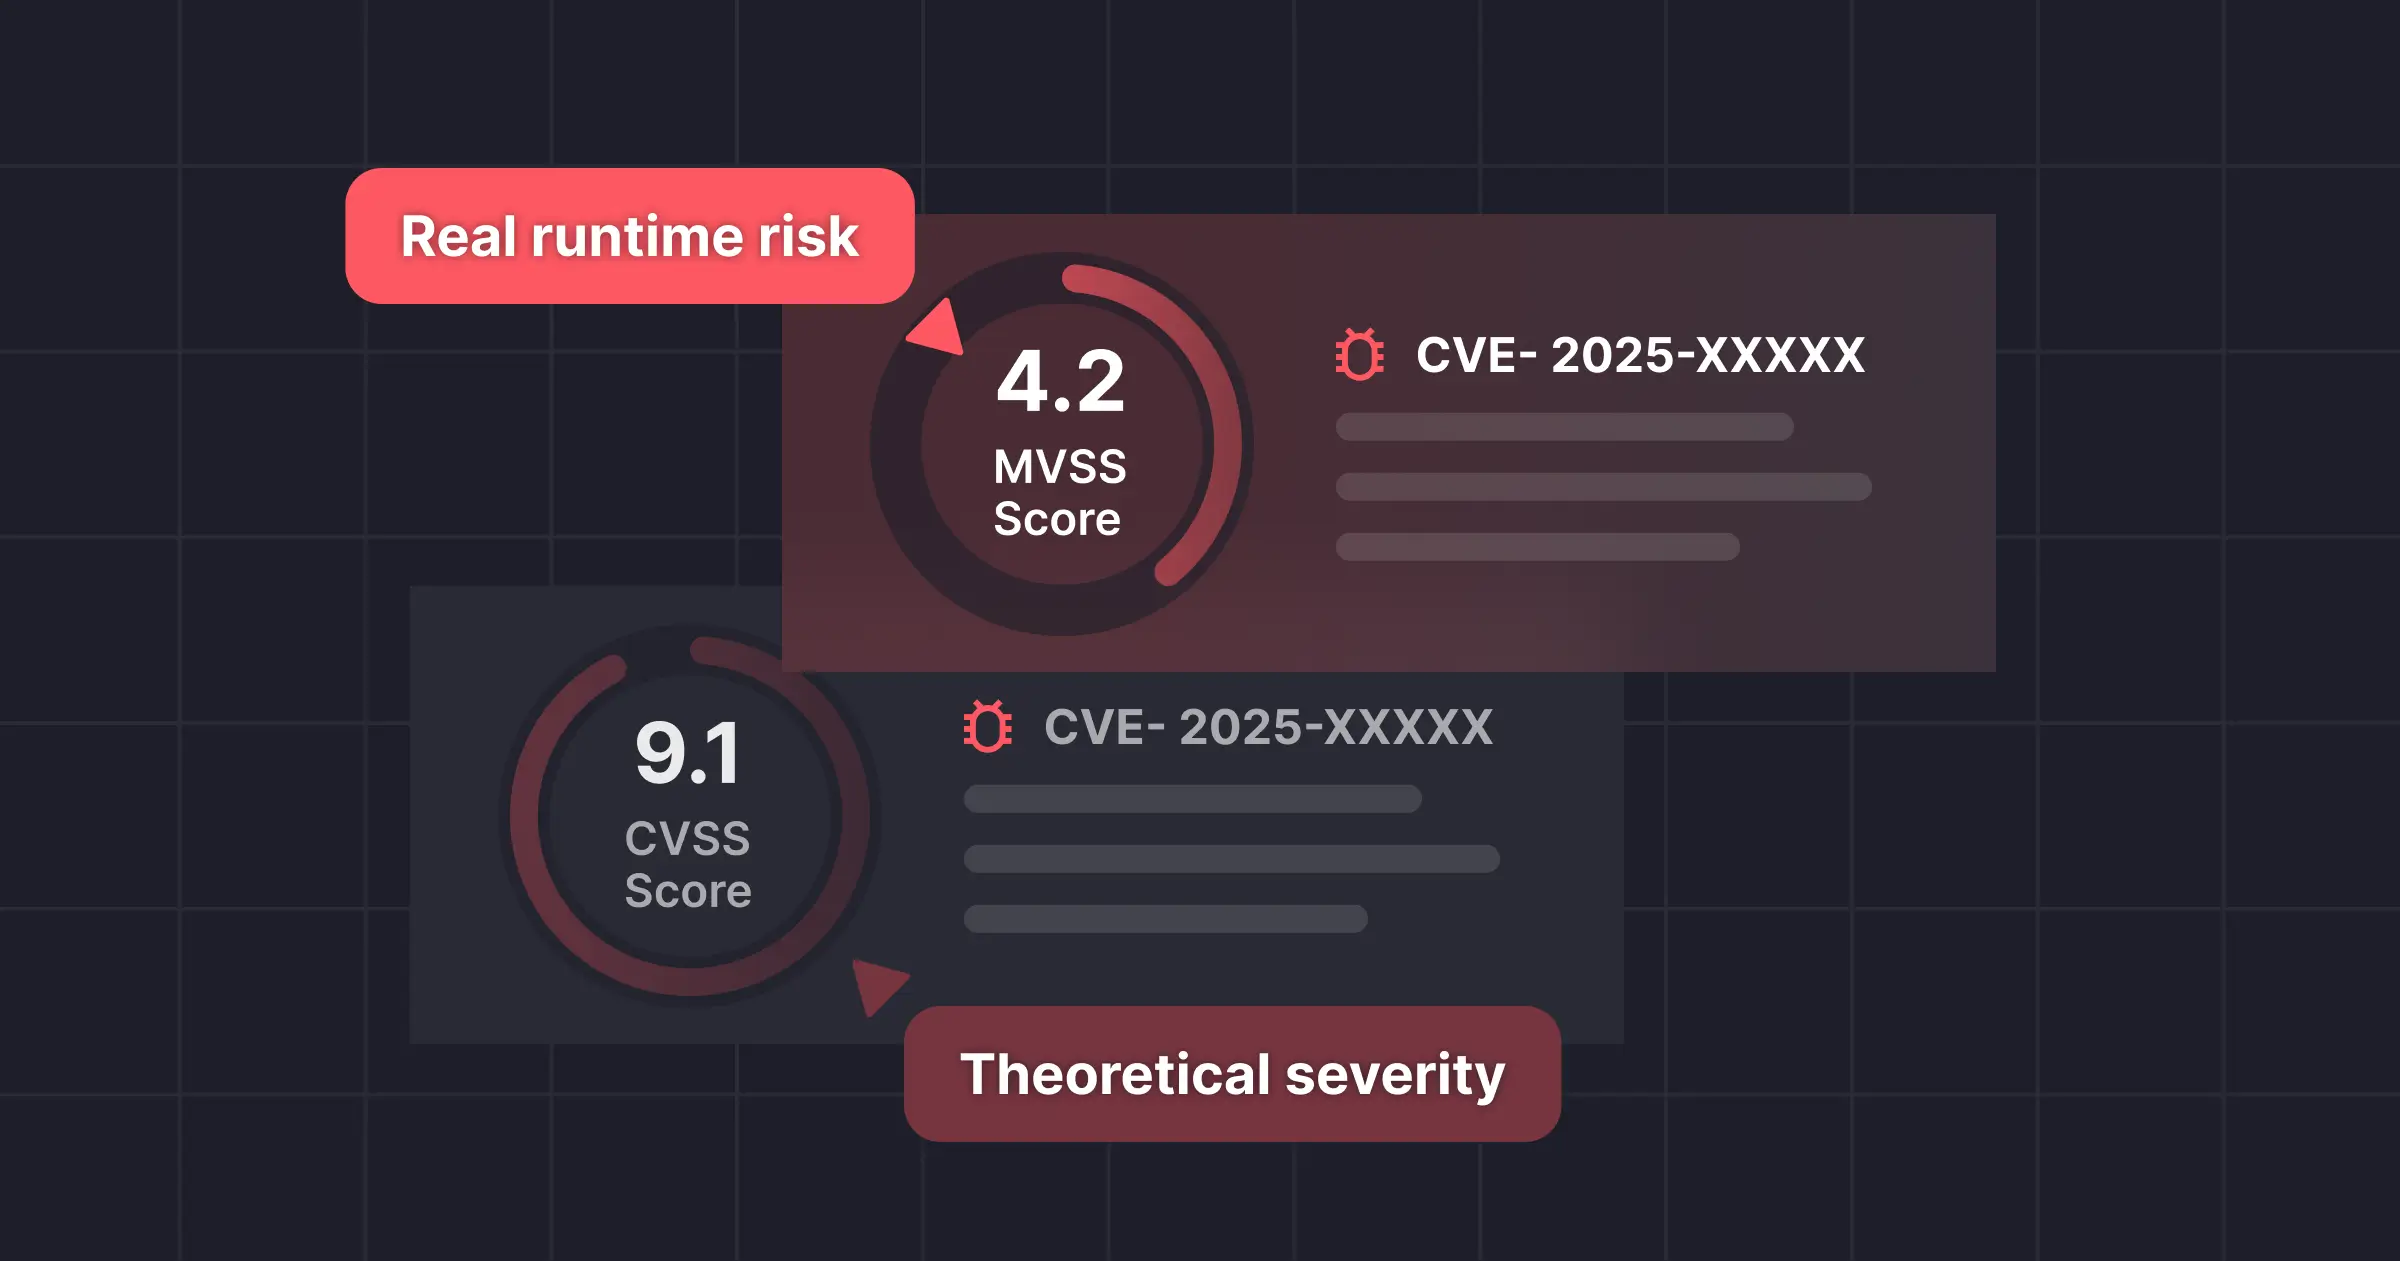
Theory vs Practice: What CVSS Can’t See
Research
Security
CVSS shows theoretical severity, but real risk exists at runtime. Learn how Miggo Risk Score cuts noise and helps teams prioritize what truly matters.
Read More
New Report: Beat the Bypass: Why 52% of Vulnerabilities Slip Past the WAF (and How AI Augmentation Fixes It)
Security
Research
52% of exploits bypass standard WAFs. Our new report reveals the $6M cost of this gap and how AI runtime defense closes it. Read the full study now.